Investigating A2P SMS Pumping: Preserve Evidence and Contain Abuse
An alert-response guide to scoping an incident, cross-checking signals, and applying proportionate measures without mistaking traffic anomalies for confirmed fraud.
An anomaly alone does not confirm SMS pumping
SMS pumping is suspected abuse involving automated message requests that can generate traffic and costs without corresponding to legitimate use. A rise in volume, concentration by destination, or change in latency may warrant an investigation, but none of these indicators alone confirms fraudulent intent.
SUTEL’s resolution on measures against smishing and vishing considers distinguishing P2P from A2P traffic, verifying its origin, and analyzing rate, volume, and symmetry patterns. These are useful dimensions for observing traffic, not universal criteria for confirming SMS pumping. The available evidence does not define general thresholds or a technical diagnostic protocol.
- Treat alerts as hypotheses that must be cross-checked against the application, authentication, and messaging platform.
- Record observed facts, possible explanations, and confirmed conclusions separately.
- Consider legitimate activity, such as authorized campaigns, product changes, or increased demand, before applying blocks.
Scope the incident before taking containment action
Set a time window that includes the start of the anomaly and a comparison period suited to the service’s usual patterns. Note when the alert began, when it was detected, and which operational changes coincided with it.
Segment the available logs by endpoint or request flow, campaign or service, destination, and request pattern. Do not assume that any particular category explains the event: document which fields are available and which are not. Also compare the traffic with periods and services that have legitimately similar behavior.
Segmentation helps limit the impact of a measure. If a signal appears only in part of a flow, a global response may disrupt legitimate users’ access without improving the investigation.
- Define the period under investigation and the source of each timestamp.
- Identify the endpoints or flows involved and the affected destinations, if that data is available.
- Note relevant campaigns, configuration changes, and product events.
- Separate suspicious segments from normal traffic without assuming that a timing coincidence proves causation.
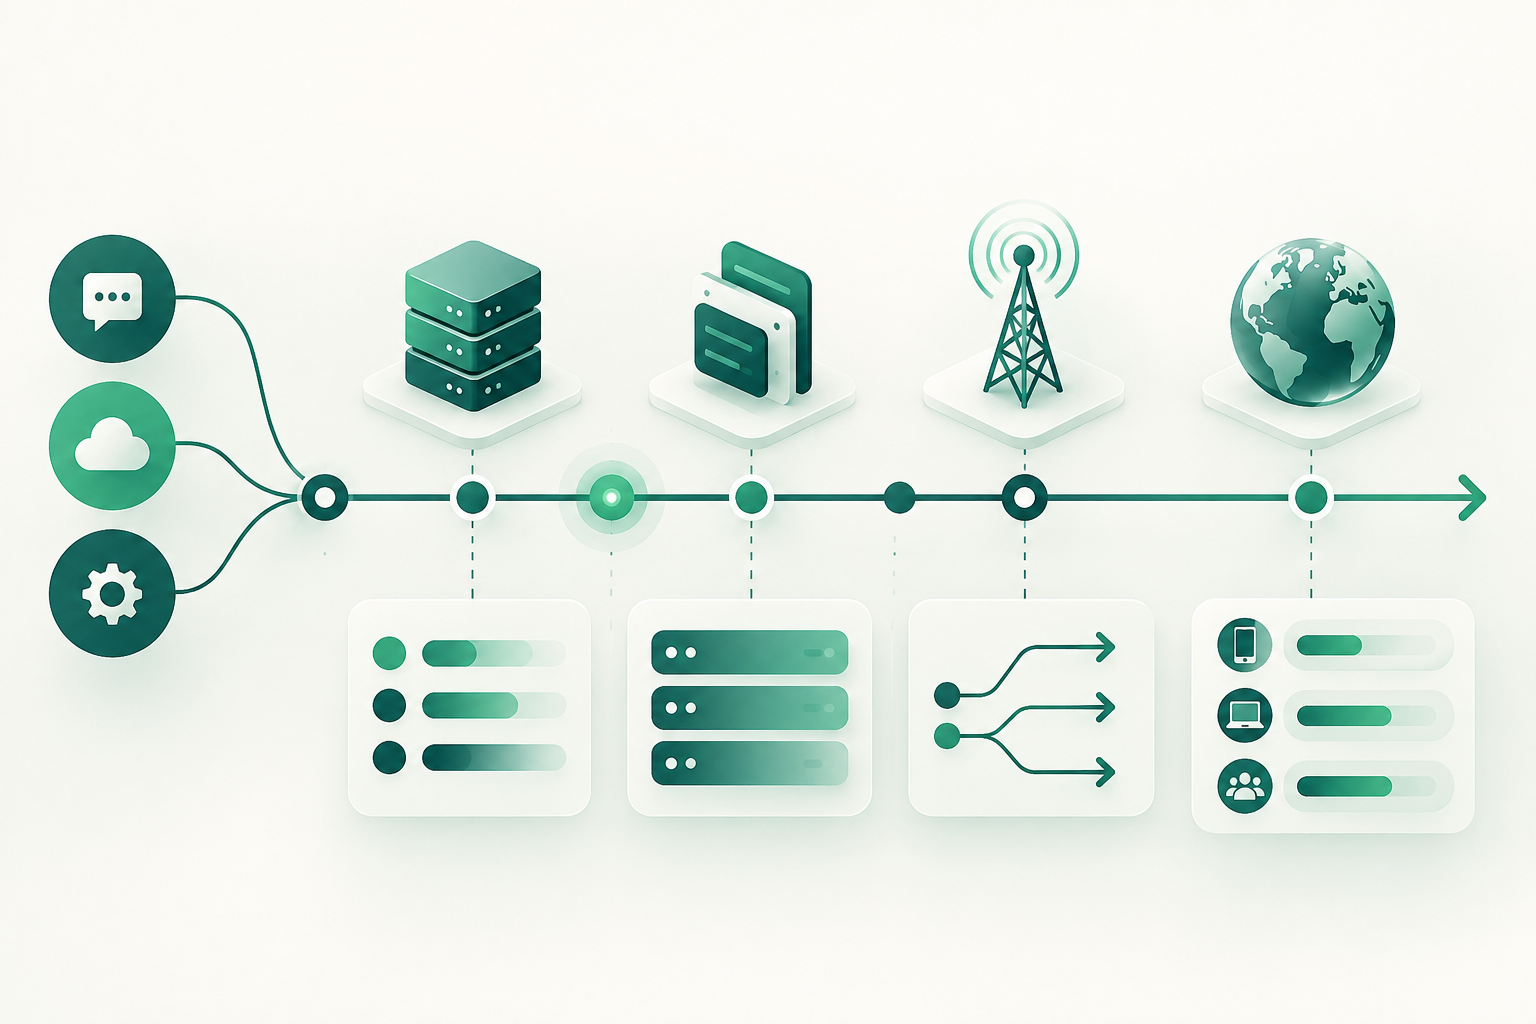
Correlate application, authentication, and SMS platform events
Compare application request events with authentication attempts and SMS platform sending logs. Look for temporal matches and relationships between events; preserve discrepancies too, since they may reveal delays, retries, or differences between systems.
A DLR reports a delivery status communicated by the messaging chain. It does not prove that a person read the message or that the original request was fraudulent. Interpretation depends on the status semantics and the information reported by each system; a provider receipt is not necessarily equivalent to independent verification of receipt on the handset.
The analysis may consider communication rate, volume, origin, and symmetry—dimensions included in SUTEL’s resolution. Interpret them in context and with awareness of the limits of available logs, not as an automatic fraud score.
- Compare request, authentication, and sending times and references where common identifiers are available.
- Distinguish initiated requests, sending attempts, DLR statuses, and authentication results.
- Document time zones, delays, and events that do not match across systems.
- Do not use a DLR status as conclusive proof of abuse, actual receipt, or user identity.
Preserve what is necessary and limit data exposure
Preserving evidence means retaining relevant logs as collected and documenting their origin, time period, and the person responsible for extraction. The available evidence does not prescribe a general chain-of-custody protocol for SMS pumping investigations; adapt practices to the legal, contractual, and security obligations applicable in each jurisdiction.
Use references that allow systems to be correlated only when needed for the investigation. Limit personal data to the minimum relevant amount, restrict access to those involved in the response, and log queries or exports in line with current internal controls. Do not inspect message content indiscriminately: SUTEL notes privacy and confidentiality concerns around SMS review, as well as the lack of general parameters for classifying a message as malicious.
In the context of the measures it describes, SUTEL’s resolution provides for retaining detailed communication records for a minimum of four years and includes documented exceptions for certain authorized A2P services. Do not apply that period automatically to every case or jurisdiction: verify its regulatory scope and the relevant retention policies.
- Record which system produced each data item, when it was extracted, and who handled it.
- Retain only the fields needed for the investigation and protect originals from unauthorized changes.
- Apply access and retention controls in accordance with applicable law and policies.
- Where practical and useful, separate operational identifiers from personal data.
Contain the incident with proportionate measures
Containment should reduce risk without turning an incomplete signal into a broad penalty. Start with the segment supported by the strongest evidence, and prefer limited, reviewable measures over blanket blocks. The specific options depend on each application and platform’s capabilities; controls are not the same everywhere.
Where possible, consider temporary limits on requests, additional authentication controls, or human review of uncertain cases. Define who can approve each measure, its expected impact on legitimate users, and when it will be reassessed. Avoid disclosing operational details that could reveal how controls are triggered.
Negative labels or warnings can also harm legitimate users and messages. The CRC has warned that incorrect negative classification can create confusion, distrust, or fatigue. Therefore, assess the user-visible impact and establish a way to correct the record if a measure affects legitimate traffic.
- Prioritize the narrowest control that reduces the observed risk.
- Define the duration, scope, owner, and review condition before enabling a measure.
- Use human review when signals are ambiguous or the cost of a false positive is high.
- Check the impact on legitimate requests, support, and access to the service.
Coordinate owners and decisions
An investigation may involve security, fraud, product, messaging operations, and the relevant provider or aggregator. Assign one person to coordinate the case and maintain a shared record of decisions, outstanding evidence, and active measures.
Share only the information each party needs for its role. Clarify who retains the logs, who can change controls, and who decides on an exception or recovery. If a provider does not have a requested field, record this as a limitation rather than treating the missing data as evidence of fraud.
- Name an incident owner and a point of contact for each participating team.
- Maintain a timeline of alerts, queries, decisions, and control changes.
- Agree what data may be shared and how it will be protected.
- Escalate legal, privacy, or user-impact concerns to the appropriate owners.
Set recovery and review criteria
Before lifting a measure, check the criteria set when it was applied: whether the signal that prompted it has changed, whether events correlate consistently, and whether legitimate traffic can resume without the same restriction. The available evidence does not support a universal recovery threshold; criteria should be tailored to the service and documented.
Lift measures in a controlled way, checking their effects and keeping a path to reinstate them if the anomaly returns. Afterwards, review which logs were missing, whether legitimate users were affected, and whether coordination between teams was sufficient. Update internal controls without turning a one-off response into an unvalidated general rule.
- Require evidence that the condition prompting the measure is no longer present or is under control.
- Check that the legitimate flow works during recovery.
- Document who authorized the lift and which signals were reviewed.
- Record lessons learned and data limitations to improve future investigations.
Frequently asked questions
Does a spike in SMS requests confirm SMS pumping?
No. It is an anomaly that may warrant an investigation, but it must be checked against the service context, application logs, authentication, and the messaging platform. The available evidence does not define universal confirmation criteria.
Does a DLR prove that the user received the message or that fraud occurred?
Not by itself. A DLR reports a delivery status based on the information available in the messaging chain. It does not prove that a person read the SMS or establish the intent behind the request.
What data should be preserved during an investigation?
Retain relevant logs from the systems involved, their timestamps and provenance, and the references needed to correlate them. Limit personal data and access in accordance with applicable legal, contractual, and security obligations.
How long should records be retained?
It depends on the jurisdiction, record type, and applicable obligations. The cited SUTEL resolution provides for a minimum of four years in the context of the measures it describes; this should not be treated as a universal period for every organization.
When should containment measures be lifted?
After reviewing the signals that prompted the intervention, confirming that the risk is controlled according to criteria defined for the service, and ensuring the legitimate flow can resume. Document the decision and monitor the effects of lifting the measure.
Sources consulted
- Resolución final sobre medidas regulatorias contra smishing y vishingSUTEL
- Documento de alternativas regulatorias para identificar y medir fraude cibernético en servicios móvilesComisión de Regulación de Comunicaciones (CRC), Colombia
- Respuesta a comentarios sobre medidas contra fraude cibernético por servicios móvilesComisión de Regulación de Comunicaciones (CRC), Colombia
- Informe de consulta pública sobre SMSSUTEL