A2P SMS Traffic Authorization: A Guide to Verifiable Decisions
Internal authorization does not replace external approvals or guarantee delivery or compliance. Learn how to define its scope, retain evidence, and review permissions when conditions change.
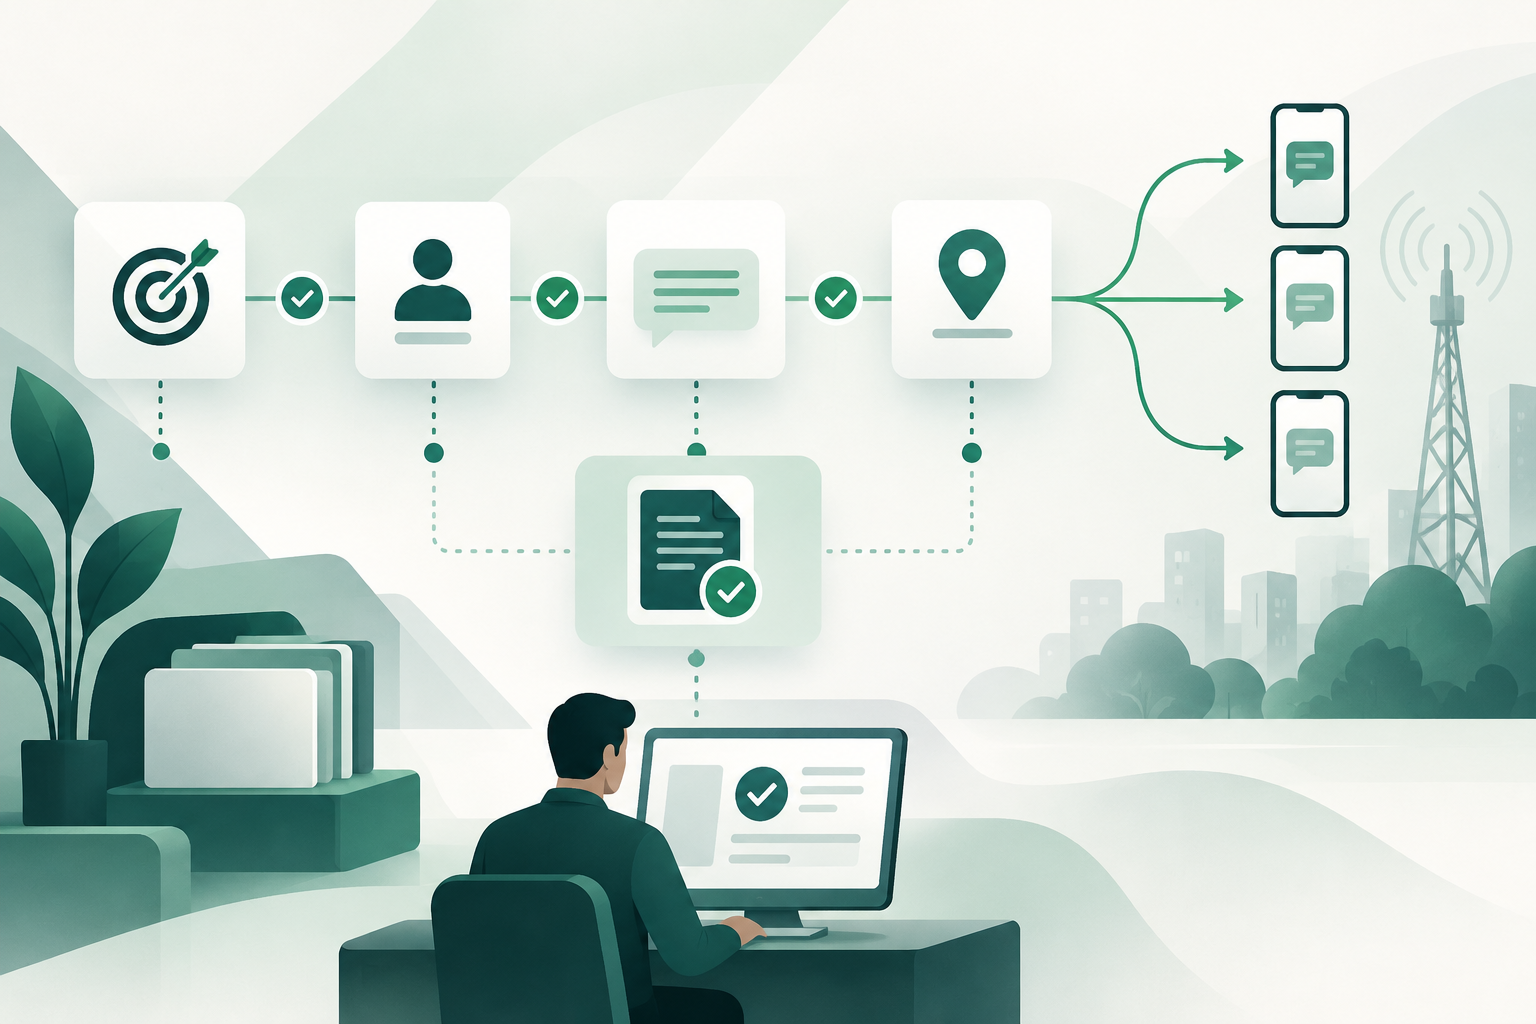
What It Means to Authorize A2P SMS Traffic
In an A2P operation, “authorization” can refer to different decisions. A company may internally approve a use; a provider or platform may enable an account or configuration; and an operator or authority may require its own processes or conditions. These are not equivalent, and one approval does not automatically replace the others.
A documented internal authorization records what was decided, who approved it, and within what limits. On its own, it does not prove that all external requirements have been met, that the content is lawful in every jurisdiction, or that a message will be delivered.
- Treat each permission as a decision with a defined scope, not as blanket approval for all of an organization’s traffic.
- Separately verify requirements that may apply to the company, provider, operator, sender, and destination.
- Do not treat a send confirmation or DLR as automatic proof that a message was received on a phone.
Define the Scope Before Approval
For an internal decision to be reviewable, specify which traffic it covers. As a control framework, record the purpose, sender identity or name, content or template reference, intended countries or destinations, provider, and validity period. These fields are an operational proposal for defining the decision’s scope, not a universal list of legal or technical requirements.
The broader the authorization, the harder it is to check whether a specific send falls within it. If you cannot describe a limit in verifiable terms—for example, which destinations are included or what content is allowed—clarify it before approval or record the uncertainty.
- Purpose: describe the intended use precisely enough to distinguish it from other uses.
- Sender: identify the approved sender and any expressly included variations, if applicable.
- Content: retain the approved template or version, or define how permissible changes are identified.
- Destination and provider: specify the geographic scope and the provider or service covered, where applicable.
- Validity and limits: set a review or expiry date and, if appropriate, operational limits defined by the organization.
Separate Internal Approval from External Obligations
Internal approval records that an organization has made a decision within its own processes. It does not, by itself, prove that valid consent exists, that a sender has been registered where required, or that the conditions applicable to each destination or route have been met.
Obligations may depend on the country, message type, the role of each entity, and operator or provider rules. The information available here does not establish specific requirements, mandatory fields, or universal regulatory deadlines. Confirm these details with relevant official documentation and the responsible parties before enabling traffic.
- Keep the record of internal decisions separate from evidence of external approvals or requirements.
- Note which official source or contact confirmed each external condition and the date it was checked.
- If there is doubt about a legal obligation, seek a qualified review for the specific destination and use; do not assume internal approval is sufficient.
Create a Reviewable Record
A useful record makes it possible to reconstruct the decision without relying on memory or scattered conversations. Internally define the fields needed to identify the authorization, its owner, supporting evidence, and status. The information available does not prescribe a universal template for every case.
Restrict access to evidence according to the organization’s needs. If you store personal information, determine how to handle it under applicable rules; a general reference to data protection does not make it possible to specify retention periods or particular obligations here.
- Identifier and status: pending, approved, suspended, revoked, or expired, according to internal categories.
- Owners: who requests, who reviews, and who has authority to approve or change the permission.
- Scope and evidence: the elements covered and the documents or records supporting the decision.
- Limits and review: operational conditions, review date, and the reason for any status change.
- History: retain a trace of changes and who made them, in line with organizational policies.
Check Traffic Before Sending
Before enabling a flow, compare its configuration and available information with the approved scope. The check should detect relevant discrepancies—for example, a different sender, a different purpose, or a destination outside the scope—and route them for review rather than automatically treating them as exceptions.
Technical details depend on each organization’s platform and architecture. Do not assume that all systems have the same fields, logs, or automated controls. Document which checks exist, which are manual, and what to do when information is missing.
- Confirm that the purpose and content type match the recorded decision.
- Compare the sender, template or version, destination, and provider with the approved limits.
- If a detail cannot be verified, follow the internal exception procedure or pause enablement until it is clarified.
- After sending, interpret receipts and DLRs according to their semantics and reliability; do not present them as independent verification of receipt on the device.
Review When Conditions Change
An approval tied to a purpose, content, or destination should not be treated as automatic authorization for any subsequent change. Define which variations require review and who can approve them. The specific criteria are an internal governance decision and may need to account for applicable external conditions.
If the purpose, sender, content, provider, or destination changes, record the change and assess whether the existing authorization remains appropriate. Do not assume a technical modification is harmless: it may alter the scope of the decision or trigger an external review.
- Identify the change and the date it is proposed.
- Compare the new scenario with the recorded scope and limits.
- Request a review when the variation falls outside the permission or cannot be clearly classified.
- Update the record and inform the teams that enable or monitor the traffic.
Suspend or Revoke When Relevant Signals Arise
Suspension may be a temporary measure to prevent further sends while an issue is clarified; revocation means the permission is no longer in force. Define who can decide on each measure, how it is communicated, and what evidence must be recorded.
Consider a review when evidence is insufficient, approved limits have been breached, or relevant changes have not been assessed. The information available does not prescribe automatic thresholds or a universal procedure: define criteria proportionate to your operation and check applicable obligations.
- Record the reason, decision-maker, affected scope, and date.
- Prevent a suspended or revoked permission from being reused by mistake in subsequent processes.
- Document what checks would allow the review to be closed and who authorizes reactivation, if applicable.
- Do not use an internal suspension as a substitute for any external notifications or measures that may be required.
An Auditable Workflow Example and Checklist
A team requests enablement of an A2P use for a specific purpose. The owner documents the proposed sender, content, destinations, and provider; attaches available evidence; and notes which external conditions have been checked. The authorized person reviews the scope and records a decision with limits, a review date, and a status.
Before enabling traffic, operations compares the configuration with the record. If a destination or content item is not covered, the permission is not expanded by inference; the case is sent for review. If a change is approved, the history is updated and the new scope is communicated. This example describes one possible internal practice, not a universal regulatory procedure.
- Is the purpose described specifically?
- Do the sender and content match what was approved?
- Are the destination, provider, and validity period defined?
- Are internal approval and applicable external conditions clearly distinguished?
- Are the owner, evidence, limits, and review date recorded?
- Is there a defined process for discrepancies, changes, suspension, and revocation?
- Does the process avoid treating a DLR or send status as independent proof of receipt?
Frequently asked questions
Does internal authorization guarantee that an A2P SMS will be delivered?
No. It documents an internal decision and its scope, but does not guarantee delivery. A DLR should not automatically be confused with independent verification that the message was received on a phone.
Does internal approval prove that legal or operator requirements have been met?
Not by itself. Requirements may vary by destination, use, and the parties involved. Verify external conditions using relevant official documentation and qualified contacts.
What information should an authorization record include?
As an operational framework, define the purpose, sender, content or template, destinations, provider, and validity period. Add the owner, evidence, limits, status, review date, and change history according to your organization’s needs.
When should an authorization be reviewed?
Review it when a relevant part of the scope changes, such as the purpose, sender, content, provider, or destination, and on the defined review date. If it is unclear whether a change is covered, route it for review before expanding the permission.
Sources consulted
- 3GPP specifications by series3GPP
- ITU-T Recommendation E.164International Telecommunication Union
- GSMA Networks resourcesGSMA
- Data protectionEuropean Commission
- NIST Digital Identity GuidelinesNational Institute of Standards and Technology