Access Permissions in A2P SMS Operations: A Review Guide
A cautious guide to inventorying access, limiting permissions, and documenting changes in A2P SMS operations—without confusing account security with message delivery.
What an access review can address
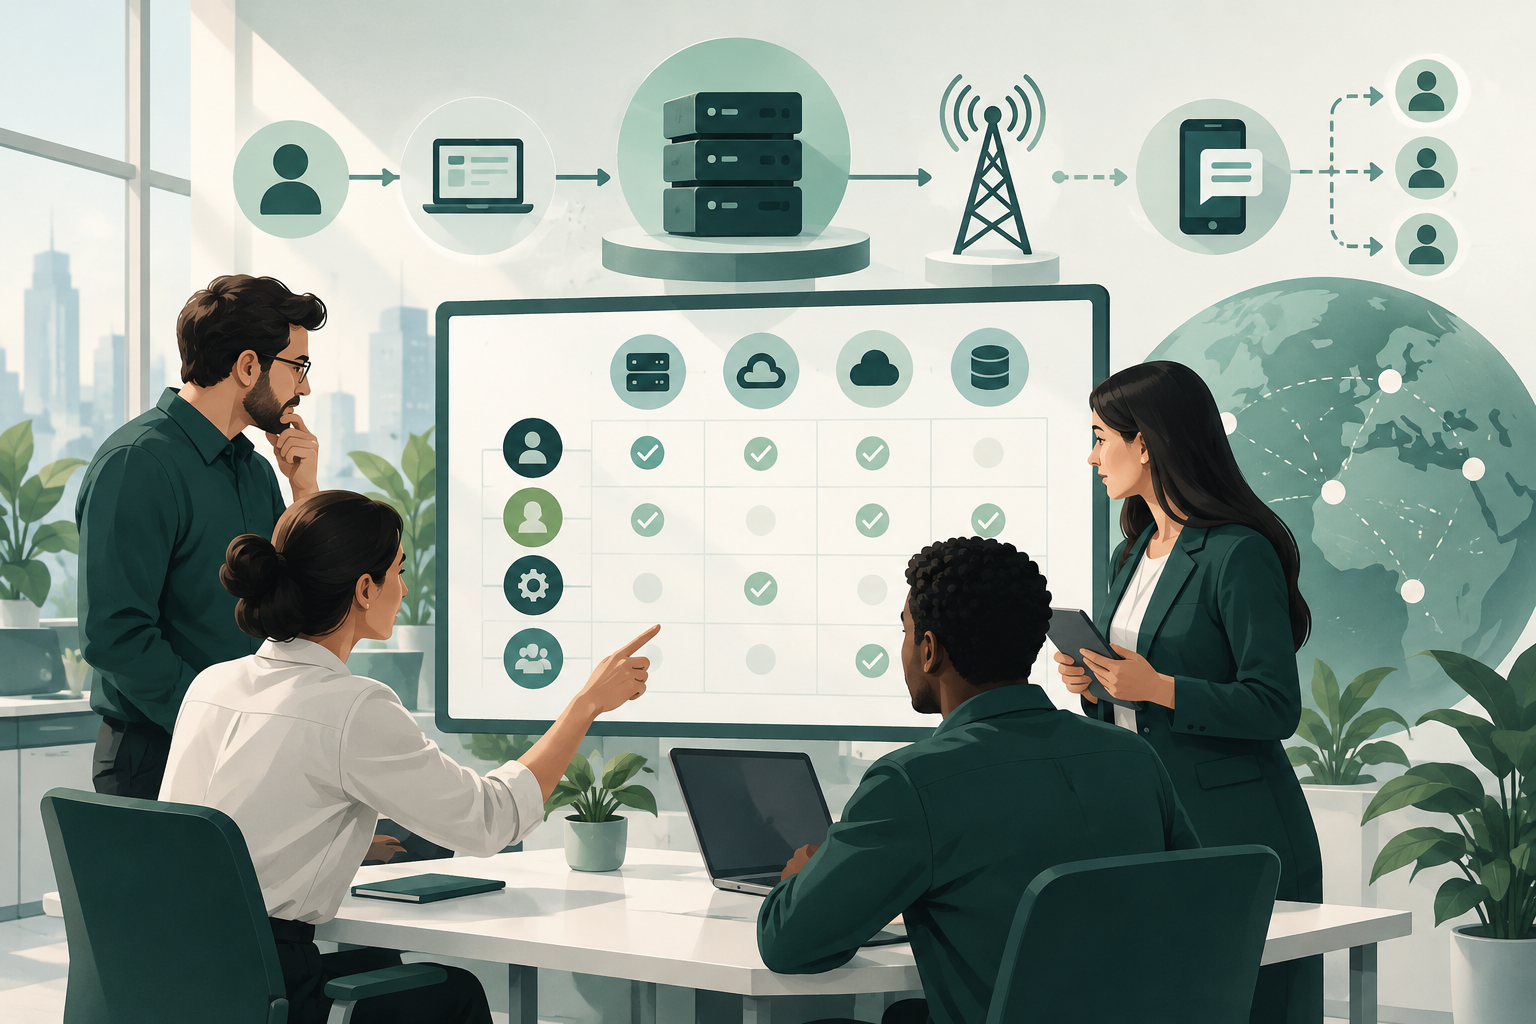
A structured review helps identify access that no longer matches current responsibilities, permissions broader than necessary, and dependencies with unclear ownership. It also provides a record of who authorized a change and what was done.
In an A2P SMS operation, access to a console, API, or management system is separate from the technical process that determines whether a message is delivered. Reviewing permissions protects systems and data; it does not verify message delivery or, by itself, improve routing, latency, or availability.
- Include only systems and access within the scope of the review.
- Do not assume that a status screen or administrative permission verifies receipt on a device.
- Define the objective and scope before changing access.
Inventory people, technical accounts, and integrations
Build an inventory that identifies who or what accesses each system. Consider individual users, service accounts, integrations, third-party tools, and vendor access, if these exist in your environment. Record only the information needed to administer and review access.
For each identity, note the owner, purpose, systems and environments it can access, assigned permissions, and how you confirm that access is still necessary. If an owner or purpose cannot be identified, record the uncertainty and assign it for resolution; do not hide it under a generic label.
- Separate human identities from technical identities.
- Link each access entry to a specific role or dependency.
- Flag shared accounts or accounts with no identified owner for analysis; do not assume they can be removed without checking dependencies.
Define roles by function, environment, and scope
Describe the tasks each role must perform and assign permissions accordingly. Where the architecture allows, keep test and production environments separate, along with the systems or traffic scopes each role can manage.
Do not assume that every platform offers granular roles, environment separation, or built-in approvals. Verify which controls are actually available and document system limitations. If a necessary capability is unavailable, record the risk and agree on an appropriate compensating measure with security and operations owners.
- Distinguish viewing, configuration, approval, and operation where the system allows.
- Limit scope to the systems, environments, and functions required.
- Do not confuse permission to configure an operation with a guarantee of delivery outcomes.
Apply least privilege using verifiable criteria
The principle of least privilege means granting only the permissions needed for an authorized task. To apply it, compare the actual responsibilities of a person or integration with each effective permission, and remove or adjust anything without a current justification after checking dependencies.
Assess permissions by action: viewing information, changing configuration, approving changes, and performing operations can have different impacts. Whether these actions can be separated depends on the system; do not claim a separation that is unavailable.
- Ask what specific task requires each permission.
- Check the affected scope and environment before reducing privileges.
- Document permissions retained because of a legitimate dependency, and identify who accepts the exception.
Organize the review with owners and evidence
Assign owners to compile the inventory, confirm that access is necessary, approve changes, and make the changes. In small teams, one person may cover more than one function, but decisions and their rationale should still be attributed.
The available evidence does not establish a universal review frequency that can be recommended for all A2P SMS operations. Set the cadence based on risk, system sensitivity, organizational changes, and applicable obligations. In addition to scheduled reviews, consider reviewing access when roles, integrations, or relationships with third parties change.
- Keep the reviewed inventory, decision, owner, and date.
- Record exceptions, their rationale, the accepted risk, and when they will be reassessed.
- Set the frequency according to the standards and policies that actually apply to your organization.
Handle team and vendor changes carefully
When someone changes roles or leaves the team, identify the access that needs to be changed or removed and check for dependent tasks, integrations, or processes. For third parties, review whether access is still needed for the agreed service and who in your organization is responsible for validating it.
The speed of revocation should reflect internal policy, applicable requirements, and risk. No single timeframe is supported here. If an account could affect production, treat the change as a priority, coordinate with operations owners, and verify the outcome to avoid both residual access and foreseeable disruptions.
- Use a checklist of systems and dependencies before closing access.
- Confirm which technical identities, credentials, or integrations require an ownership change or review.
- Record any delay, exception, or temporary measure, along with its owner.
Document approvals, changes, and revocations
Keep a record that makes it possible to reconstruct the decision: affected identity, system, permissions before and after, reason, approver, implementer, and date. Include the outcome of post-change verification where possible. Protect these records in accordance with applicable security and retention policies.
Do not assume that every platform provides complete auditing or event exports. Check what evidence each system can provide, and fill any gaps with a controlled operational record if internal policies permit.
- Link each change to an identifiable request or reason.
- Distinguish approval from the actual implementation of the change.
- Identify systems with limited traceability and agree on how to manage that limitation.
Verify access without causing an outage
After a change, check that the authorized identity retains the necessary functions and that the identity whose access was removed can no longer perform the revoked actions. Use the mechanisms available and follow your organization’s change procedure. In production, coordinate verification to reduce the risk of affecting legitimate operations.
The review may include looking for inactive or ownerless accounts if the systems provide sufficient information. Do not assume that automated alerts, uniform logs, or comparable indicators exist across platforms; validate each capability before adding it to the procedure.
- Record the outcome and any discrepancy between the requested change and what you observed.
- Escalate unexplained access and verification limitations.
- Treat access controls and SMS delivery indicators as separate areas.
Frequently asked questions
How often should permissions in an A2P SMS operation be reviewed?
There is no universally supported frequency for all environments. Set one based on risk, internal policies, and applicable requirements, and also review access when roles, systems, or third-party relationships change.
Does an access review guarantee that SMS messages will be delivered?
No. The review concerns who can access or change systems. It does not guarantee message delivery or prove receipt on a device.
What should I do if a technical account has no clear owner?
Record the account, investigate its purpose and dependencies, and assign an owner to decide whether it should be retained, changed, or removed. Do not delete it blindly if it may support a legitimate integration.
Do all platforms allow viewing, configuration, and approval permissions to be separated?
Do not assume so. Check each system’s actual capabilities and document limitations. If a necessary separation is unavailable, assess compensating measures with the relevant owners.
Sources consulted
- NIST Digital Identity Guidelines (SP 800-63-4)NIST
- European Commission: Data protectionEuropean Commission
- 3GPP specifications by series3GPP
- GSMA Networks resourcesGSMA
- ITU-T Recommendation E.164International Telecommunication Union
- Google Play SMS and Call Log permissions policyGoogle