Rotating A2P SMS Provider Credentials: An Operational Guide
General guidance for organizing changes to HTTP and SMPP credentials. The available evidence does not support a specific procedure for A2P SMS providers; confirm each step with your provider and the teams responsible.
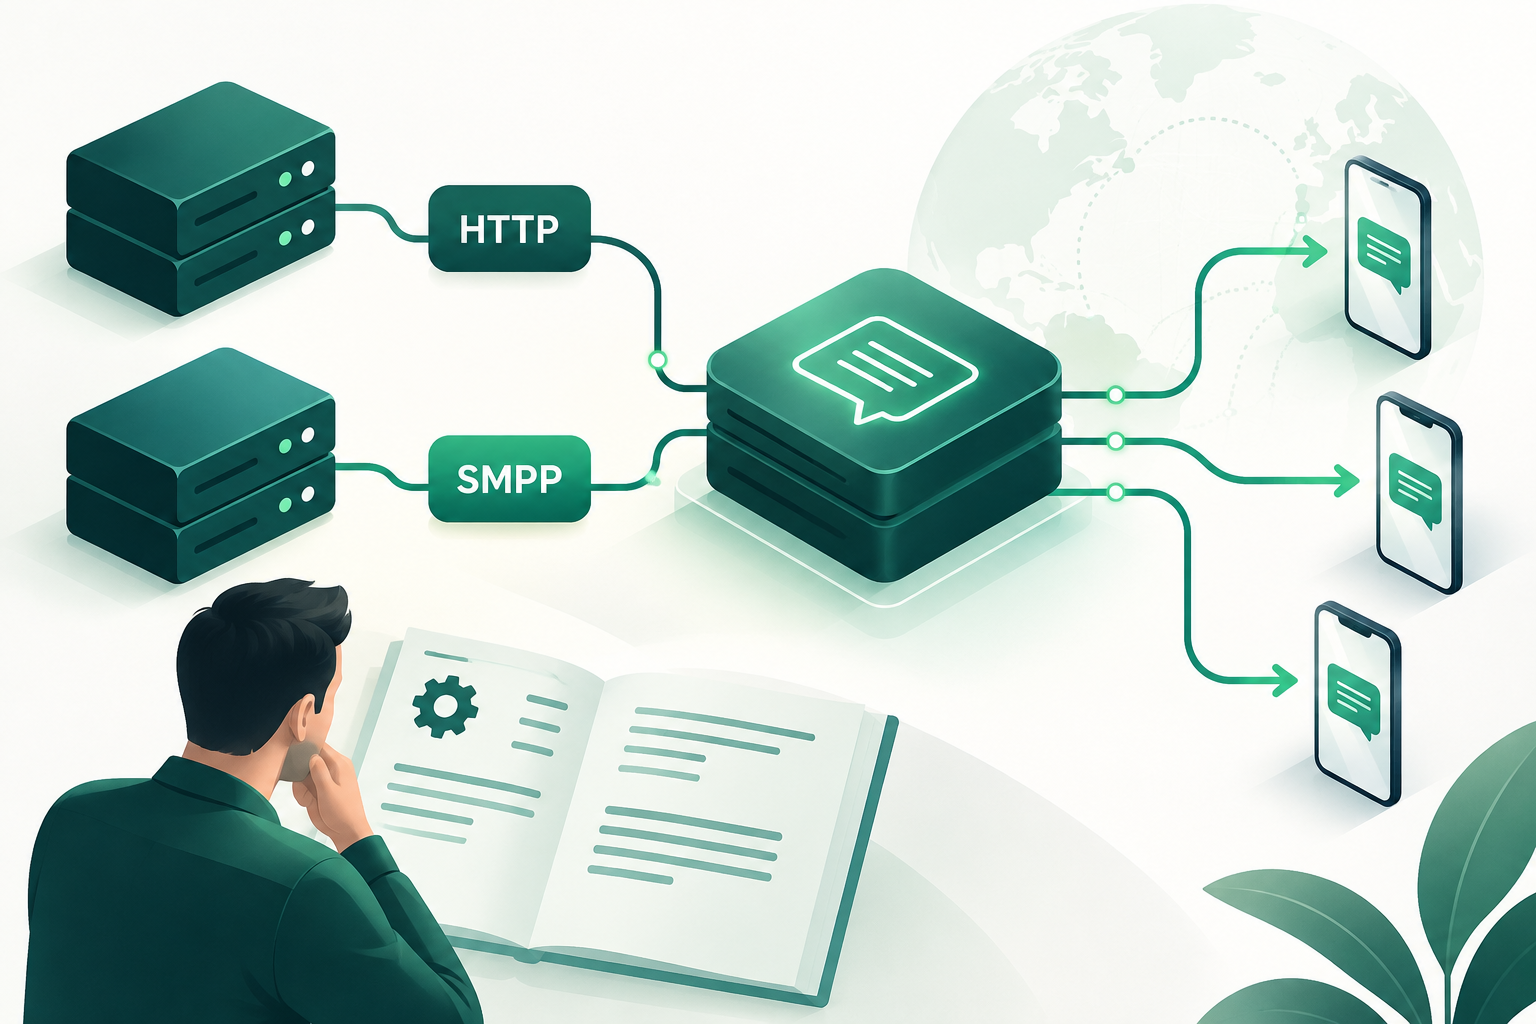
Scope of This Guide and Limits of the Evidence
This article provides general guidance, not a rotation procedure specifically supported for A2P SMS providers. The available evidence does not directly document steps for inventorying credentials, separating access, planning changes, validating connections, revoking secrets, or responding to an exposure in this context.
The SMPP specification may serve as a protocol reference, but the available evidence does not show that it establishes a credential rotation process. RFC 9110 addresses HTTP semantics; no evidence has been provided that it defines API secret rotation practices either. The available Microsoft guidance concerns Operator Nexus and does not support generalizing its steps to A2P SMS providers.
- Do not treat this guide as official provider instructions or as a validated technical procedure.
- Consult documentation applicable to your account, connection, and environment before making changes.
- Confirm with the responsible teams which steps are appropriate for your integration.
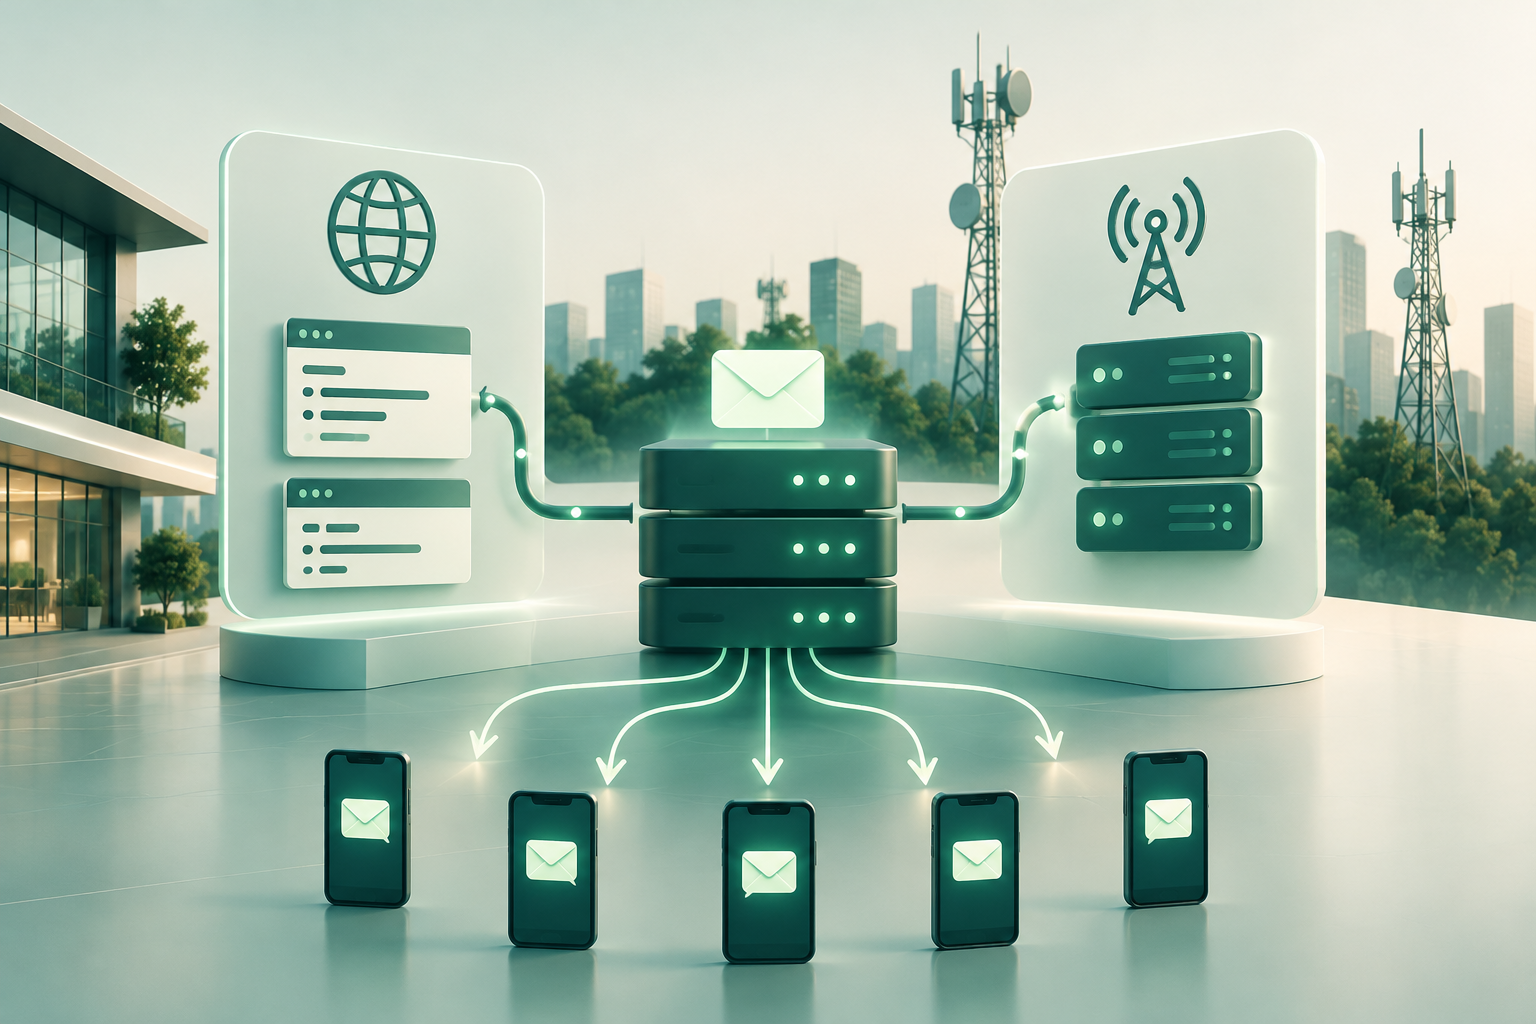
What to Confirm Before Making a Change
Before scheduling a rotation, request instructions from the provider that are specific to the affected connection and environment. The supplied evidence does not establish how a new credential is created, whether it can coexist with the old one, how it is revoked, or what post-change checks are available.
Planning and checks will depend on the provider's documentation and the integration's configuration. Do not assume that a replacement will be transparent or that the change can be rolled back.
- Identify whether the connection uses HTTP, SMPP, or another mechanism documented by the provider.
- Ask which steps the provider recommends for replacing and revoking the credential.
- Confirm whether temporary coexistence is supported and what signals can be used to check the change.
- Clarify what to do if the change causes problems; do not assume rollback is available.
Dependencies, Responsibilities, and Internal Controls
The available evidence does not directly support a procedure for dependency inventory, credential separation, least privilege, or traceability for A2P SMS providers. If your organization has internal controls for managing secrets, follow its policies and confirm with the responsible teams how they apply to the specific connection.
Do not include secrets in coordination documents, tickets, or logs unless an approved policy and an appropriate system explicitly provide for it. Applicable practices should be established with the responsible teams, not inferred from the cited protocol references.
- Ask the technical and security leads what connection information should be recorded.
- Follow internal policies for storing credentials and restricting access to them.
- Do not assume the provider offers separate credentials, configurable permissions, or automated rotation.
Validation, Revocation, and Exposure: Follow Applicable Instructions
The supplied evidence does not support specific steps for validating an A2P SMS connection after changing credentials, revoking the previous access, or preserving evidence of an exposure. Request relevant instructions from the provider and coordinate the work with the integration leads and your organization's internal processes.
If you suspect a credential has been exposed, use your internal incident response process and contact the provider. Do not interpret an accepted request or a reported DLR as independent proof that the message was received on the phone.
- Confirm with the provider which checks are available for your connection.
- Clarify how and when the previous credential should be revoked, if applicable.
- In the event of a possible exposure, follow your internal process and coordinate the response with the provider.
- Distinguish results reported by the integration from independent verification of receipt on the device.
Documenting the Change
The available evidence does not specify what change records should be kept for rotating A2P SMS provider credentials. Consult your organization's policies for documenting authorization, checks, issues, and communications with the provider.
Record any visibility limitations or outstanding steps in accordance with internal procedures. Do not present the change as validated if the relevant checks have not been confirmed.
- Follow internal policies for documentation and protecting sensitive information.
- Record outstanding questions and who is responsible for following up, in accordance with the applicable procedure.
- Do not include credentials in clear text in the change record.
Frequently asked questions
Do HTTP and SMPP require the same rotation procedure?
The available evidence does not establish a credential rotation procedure for A2P SMS providers based on the HTTP or SMPP references. Consult the provider's instructions for your specific integration.
Can I keep the new and old credentials active at the same time?
The supplied evidence does not establish that an A2P SMS provider supports this option. Confirm it with the provider before planning the change.
What shows that the change has been validated?
The available evidence does not specify a validation method. Confirm with the provider which checks apply to your connection. An accepted request or a reported DLR does not necessarily prove that the message was received on the phone.
What should I do if I suspect a credential has been exposed?
Follow your internal incident response process and coordinate actions with the provider. The supplied evidence does not support a specific sequence for containment, revocation, and replacement for A2P SMS providers.
How can I check that no system is still using the old credential?
The available evidence does not establish what usage signals each provider offers. Consult the applicable documentation and the integration leads; do not claim that the absence of consumers has been demonstrated without sufficient visibility.
Sources consulted
- SMPP Protocol Specification v3.4, Issue 1.2SMPP Developers Forum
- HTTP Semantics (RFC 9110)IETF
- Credential rotation for Operator NexusMicrosoft Learn