How to Approve New A2P SMS Routes with Evidence, Owners, and Reversal Criteria
An auditable workflow for approving A2P SMS routes: define the actual scope, separate claims from observed evidence, run limited pilots, interpret DLRs carefully, and suspend a route when operational signals justify it.
What operational risk does an A2P SMS route approval workflow address?
Approving an A2P SMS route should not simply mean adding a country to a coverage table or enabling credentials. A useful approval turns a routing decision into a reviewable record: it defines what was authorized, under which conditions, with what evidence, who accepted each decision, and what must happen if subsequent behavior is no longer acceptable.
This workflow reduces several common risks: enabling a capability that does not support the intended traffic, confusing a commercial claim with technical validation, attributing the result of a limited test to an entire route, or having no accountable owner able to suspend traffic during an incident.
The goal is not to promise future delivery. It is to establish an operational basis for deciding whether a specific configuration may enter a controlled pilot and, later, whether there is sufficient evidence to maintain, expand, suspend, or reverse its use.
- Avoid approving based on price or a generic coverage claim.
- Keep traceable evidence of every test and every subsequent change.
- Retain assumptions and limits: a test represents only the scope, configuration, and time window in which it was performed.
- Assign in advance who can expand, pause, or reverse the activation.
The approval unit: separate destination, carrier, traffic type, Sender ID, and usage conditions
The approval unit should not be a country alone. International numbering makes it possible to identify and analyze destinations for routing, but a national coverage label alone does not retain the attributes needed to reproduce an operational decision.
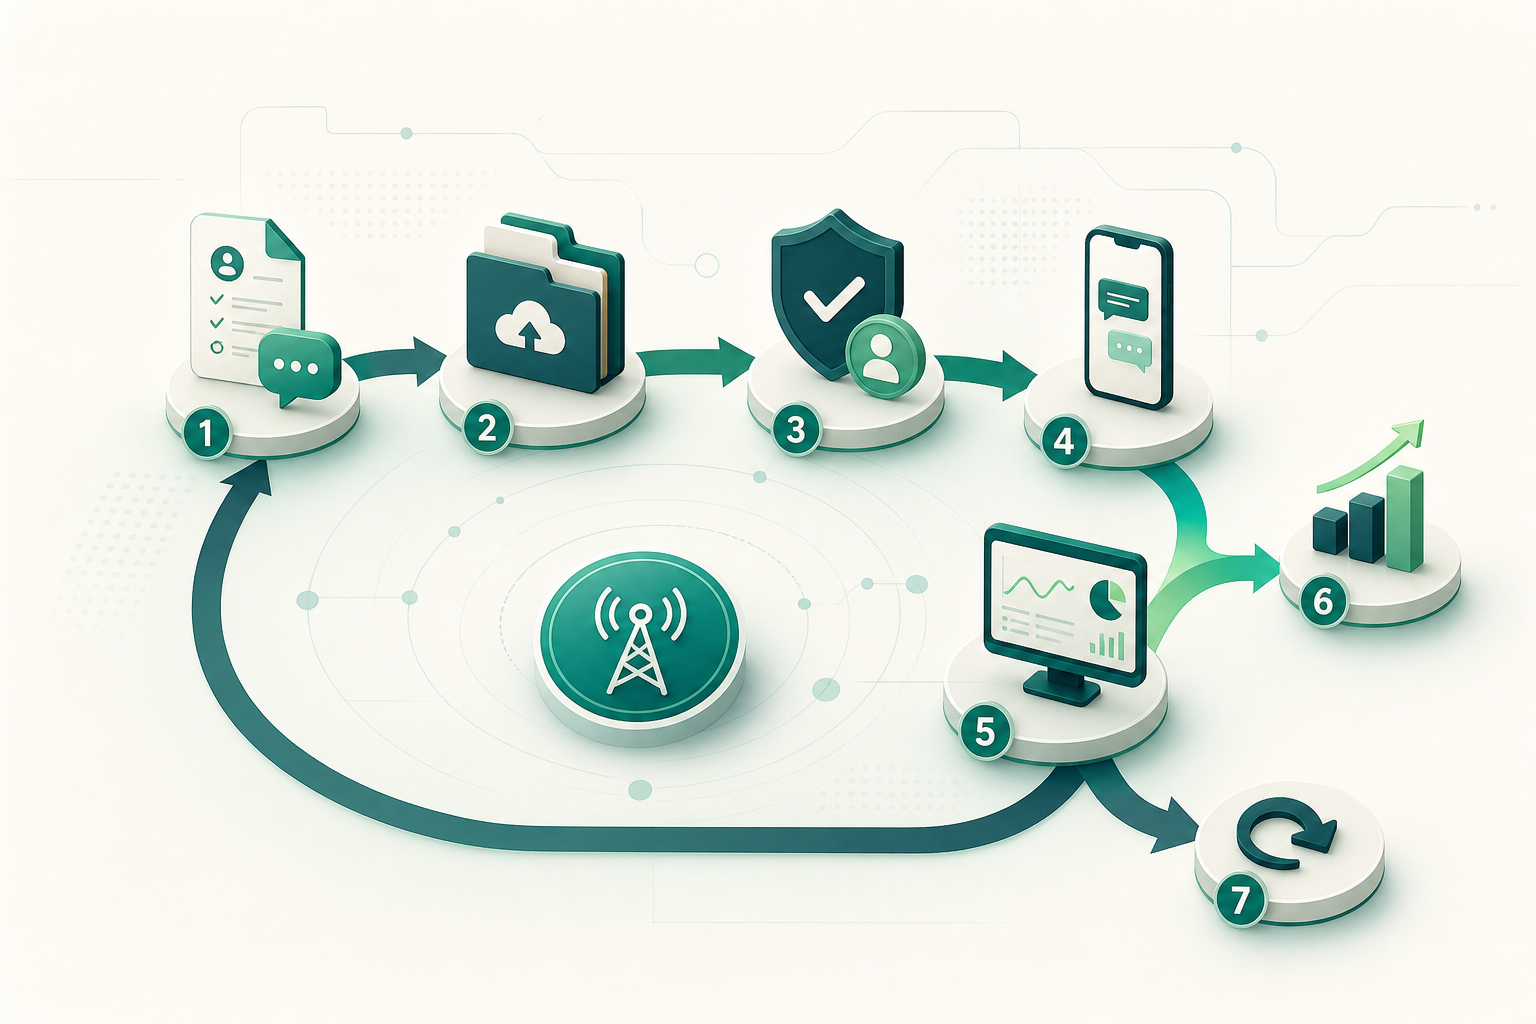
Define each approval at the most precise level available. At a minimum, record the normalized destination, network or routing condition when known, traffic type, authorized sender or origin, and usage restrictions. If the destination network cannot be determined before sending, explicitly document that limitation and do not present the approval as valid for every carrier in the country.
Also separate use cases. OTPs, transactional alerts, and legitimate marketing campaigns may be subject to different operational and compliance requirements. Approval for one traffic type does not automatically authorize another.
- Normalized destination, including the numbering convention used.
- Destination carrier or routing condition, when available.
- Authorized traffic type.
- Permitted Sender ID, originating number, or other sender identity.
- Content, consent, opt-out, and usage-window restrictions where applicable.
- Initial volume limits and any excluded destinations.
Roles and responsibilities: who requests, validates, and approves
A route should not be approved because one person sent a successful test. Separation of responsibilities reduces the risk that a commercial decision overlooks technical restrictions or that a technically functional configuration is used for traffic that does not meet applicable conditions.
The requester describes the need and scope. The technical validator checks connectivity, configuration, and traceability of results. Compliance reviews the intended use where consent, opt-out management, or other restrictions apply. The commercial owner confirms purchase or sales conditions, while the final approver accepts the operational risk within the defined limits.
The authority to suspend must be assigned before the pilot. During an incident, waiting for ad hoc approval to stop traffic may increase the impact.
- Requester: submits the use case, scope, destinations, and traffic type.
- Technical validator: verifies connection, authentication, message correlation, and observed statuses.
- Compliance owner: validates consent, opt-out, senders, and applicable restrictions where relevant.
- Commercial owner: confirms operational conditions and restrictions stated by the counterparty.
- Final approver: authorizes the pilot or activation within the documented scope.
- Operations owner: monitors the route and performs suspension or reversal according to the plan.
Minimum evidence before activating a route
Keep the provider’s statement separate from observed evidence. The former records what the counterparty claims to support or authorize. The latter records what the team actually verified on a specific date, configuration, and scope. Both are necessary, but they answer different questions.
Before activating a route, retain the documented restrictions, connectivity configuration used, tested sender identity, permitted test content, and identifiers that allow each submission to be correlated with subsequent events. In HTTP or SMPP environments, this includes the request or message identifier, timestamps, submission responses, and available DLRs or callbacks.
The technical SMS specification describes how the service works, but it does not confirm that a specific commercial route is active or that it supports every combination of sender, content, volume, or traffic. Evidence must therefore refer to the specific route and conditions being authorized.
- Dated provider statement attributable to the provider.
- Documented known restrictions and usage conditions.
- Connection configuration and authentication method used during testing.
- Correlatable identifiers for each message.
- Submission timestamp, acceptance response, and subsequent events.
- Record of destination, sender, traffic type, and test content.
- Outcome of exceptions, rejections, or missing final events within the defined window.
What controlled tests can demonstrate, and what they cannot
A controlled pilot can demonstrate that a specific configuration was able to connect, authenticate, submit messages, and receive certain statuses during a test window. It can also reveal restrictions by destination, sender, content, or configuration.
It does not demonstrate a guarantee of future delivery, stable capacity, or universal acceptance. Messages may move through intermediate and final statuses, and systems may report results such as throttling, temporary failures, permanent failures, carrier blocking, content filtering, or unknown outcomes. These behaviors justify limiting what can be extrapolated from a test.
Design the pilot to learn, not to certify absolutely. Test only legitimate, consented traffic that is compatible with the approved restrictions. Record the exact conditions so the result can be interpreted without improperly extending it to other cases.
- A test is not equivalent to a future contractual or technical guarantee.
- A result for one carrier or destination does not automatically represent all national destinations.
- A tested Sender ID or content does not validate other senders or templates.
- The absence of a final event requires analysis of the reporting window and provider semantics before concluding there was a failure.
- Later changes to the provider, connectivity, or policy invalidate part of the historical evidence.
Submission statuses and DLRs: useful signals, not automatic proof of handset receipt
Delivery statuses must be interpreted according to the semantics documented by the provider and network. An upstream acceptance or “sent” status indicates that the next provider or carrier accepted the message for further processing; it does not by itself confirm final delivery.
Even a DLR marked delivered should not automatically be treated as independent observation of receipt on a test handset. It may be based on confirmation from the upstream carrier and, when available, information from the handset. The approval record should retain the definition applicable to the received status.
Where feasible and appropriate, an independent check on a test device can supplement DLRs. It must be recorded as separate evidence: it confirms the observation on that handset, with that SIM, device, location, and time; it does not turn the result into a general guarantee for the route.
Delayed or missing final events also do not automatically mean the message was not delivered. Some carrier-generated events may arrive late, and an unknown status may indicate that the provider does not know the final outcome.
- Distinguish submission acceptance, DLRs, and independently observed receipt.
- Retain the definition of every status used by the provider or connection.
- Do not draw quality conclusions from a single isolated status.
- Define an observation window before classifying delayed or missing events.
- Investigate pattern changes by destination, sender, content, and traffic condition.
Layered acceptance criteria
Binary criteria often hide problems. It is better to approve in layers, so that a route advances only if it meets the applicable conditions at each level. This makes it possible to distinguish a connectivity incident from a content restriction or a DLR reporting issue.
Internal thresholds should be defined by authorized parties according to the use case, risk, and available evidence. Universal figures should not be applied without context. What matters is that the criteria are established in advance, versioned, and measurable using the available records.
- Layer 1, connectivity: connection, authentication, and configuration are functional.
- Layer 2, acceptance: correlated message submission responses with no unexplained rejections.
- Layer 3, statuses: consistent receipt and reconciliation of callbacks or DLRs according to their semantics.
- Layer 4, behavior: review of exceptions by destination, sender, content, schedule, or test condition.
- Layer 5, compliance: confirmation that traffic and consent or opt-out mechanisms meet applicable conditions.
How to document restrictions and design a gradual activation
Every known restriction should be associated with the route, rather than kept only in emails, conversations, or individual knowledge. The route policy should state which traffic it accepts, which senders may be used, which content is permitted, which destinations are excluded, and which operational limits apply.
The initial activation should have limited scope. Define the destinations, senders, and traffic types included; set a volume limit; enable monitoring; and establish a formal decision point. At that point, authorized people decide whether to expand, maintain the pilot, suspend, or reverse it.
Where applicable, compliance should validate before the pilot that traffic has the necessary consent basis and that effective opt-out request management mechanisms are in place. Technical enablement of a route does not replace these obligations.
- Permitted and excluded traffic types.
- Approved senders and conditions for changing them.
- Content restrictions and test templates.
- Excluded destinations, carriers, or ranges when known.
- Time windows and initial volume limits.
- Monitoring period and decision-point date.
- Operational owner during the pilot.
Frequently asked questions
Does a successful test allow a route to be approved for an entire country?
Not necessarily. A test represents the observed destinations, known carriers, senders, content, configuration, and time period. The approval should retain that scope and should not automatically be extended to every carrier or traffic type in the country.
Does a delivered DLR confirm that the user received and read the SMS?
No. A DLR is a delivery signal with semantics defined by the provider and network. It may be based on confirmation from the upstream carrier and, when available, the handset. It does not automatically prove independently observed receipt or that the recipient read the message.
What should trigger suspension or reversal of a route?
The policy should define signals and responsible owners before launch. Examples include permanent errors, carrier or content blocking, an increase in unknown outcomes, loss of callbacks or DLRs, breach of approved restrictions, or unauthorized configuration changes. The immediate action should include pausing affected traffic and preserving the evidence.
When should an A2P SMS route be revalidated?
After material changes to the provider, connection, credentials, sender, content policy, destinations, stated restrictions, DLR behavior, or observed incidents. Previous evidence relates to a specific configuration and period.
What should a route decision template contain?
Version, date, exact scope, provider statement, restrictions, tested configuration, evidence sources, identifiers and timestamps, assumptions, accountable owners, approvals, pilot limits, monitoring rules, suspension criteria, and the reversal procedure.
Sources consulted
- 3GPP TS 23.040 — Technical realization of the Short Message Service (SMS)3GPP
- ITU-T E.164 (02/2026) — The international public telecommunication numbering planInternational Telecommunication Union
- SMPP Protocol Specification v3.4, Issue 1.2SMPP Developers Forum
- SMPP Delivery Receipt FormatSMPP Developers Forum
- Messages resource — status values and callbacksTwilio
- Outbound Message Status in Status CallbacksTwilio
- Best Practices for Messaging Delivery Status LoggingTwilio
- SMS event data stream from Amazon PinpointAmazon Web Services
- Troubleshooting the SMS channelAmazon Web Services
- SMS Delivery Receipts API GuideVonage
- Retrieving Delivery ReportsSinch
- FCC 24-24 — Revocation of consent for robocalls and robotextsFederal Communications Commission