A2P SMS Route Provenance: What to Ask a Provider and How to Verify What Can Actually Be Proven
An operational guide to assessing the declared provenance of an A2P SMS route, documenting its restrictions, and separating commercial, contractual, and technical evidence without confusing them with delivery guarantees.
Why Route Provenance Matters
A2P SMS route provenance is a procurement, operations, quality, and compliance control. Its purpose is not to obtain a generic delivery promise, but to understand what has been declared about a route, within what scope, which restrictions apply, and what evidence can be retained for operations and incident investigation.
Documented provenance helps inform decisions on capacity, Sender ID handling, permitted traffic types, failure escalation, and changes in conditions. It also reduces the risk of interpreting a commercial label as though it fully described the technical behaviour of every destination.
Observed quality remains necessary, but it does not replace documentation. A route may show useful operational results during a test and still not disclose every participant in its commercial or technical chain.
- Separate the provider's claim from the evidence supporting it.
- Define the scope by country, destination network where known, traffic type, and effective date.
- Record restrictions before enabling production traffic.
- Treat any material change as a controlled route change.
What Provenance Means in A2P SMS
Provenance should be assessed across three distinct areas. The first is the commercial chain: the immediate provider and any intermediaries that are known or declared. The second is the technical chain: the interconnection architecture and functions involved in routing. The third is destination conditions: the applicable terminating network or entity, declared coverage, authorised traffic, accepted senders, limits, filtering, time windows, and support rules.
A number in E.164 format provides international addressing structure, but it does not by itself prove which applicable terminating network or entity will receive the message, nor which provider chain has been used. Number portability is an additional reason not to infer the current terminating network solely from a prefix.
To verify country, numbering plan, and administrative data, it is advisable to consult the relevant national administration's sources or the ITU repository of national numbering plans. Commercial prefix tables may be useful as an operational reference, but they should not be the sole basis for validation.
- Commercial chain: immediate provider, declared relationship, and known intermediaries.
- Technical chain: architecture and functional points relevant to operations.
- Destination conditions: rules applicable to traffic within a specific scope.
- Numbering evidence: national sources or the ITU repository when relevant.
What Direct, Hub, and Intermediated Labels Describe
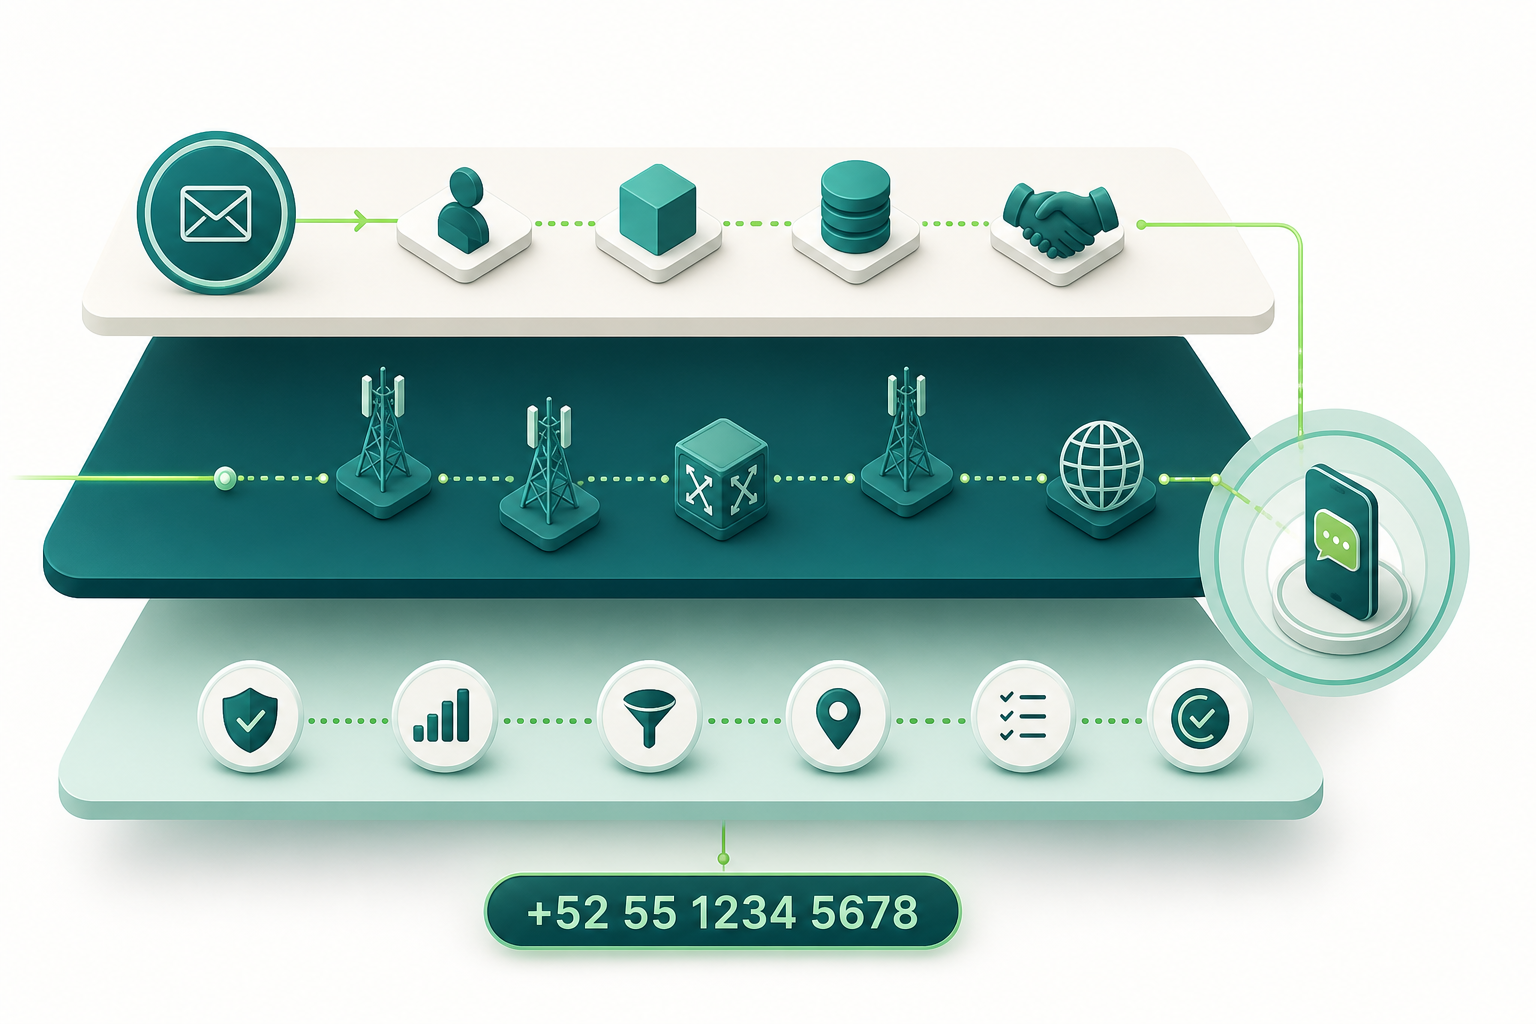
The labels direct, hub, and intermediated can be useful if their meaning is defined. On their own, they do not constitute universal proof of topology, contract, or quality. A direct route claim should specify the destination, applicable terminating network or entity it refers to, who makes the claim, which traffic it covers, and the period during which it applies.
A hub label may describe an interconnection architecture through an aggregator. It does not automatically mean that the provider has a direct contractual relationship with every destination terminating network or entity. Likewise, intermediated describes the presence of one or more segments between the immediate provider and the destination, but it requires an operational scope to be useful.
Avoid accepting vague definitions such as global direct or premium without a destination matrix, restrictions, and conditions. The label should be an attribute of a route record, not a substitute for that record.
- Destination: country and, where known, the applicable terminating network or entity.
- Scope: traffic type, sender, content, and applicable conditions.
- Declarant: entity making the claim and date of issue.
- Validity: effective date and review date or condition.
- Limitations: undisclosed information, technical restrictions, and known exclusions.
The Four Types of Evidence That Must Not Be Confused
A robust assessment distinguishes four types of evidence. The provider statement communicates what the provider claims. The contract or commercial addendum may establish obligations, scope, and change mechanisms between the parties. Operational documentation explains how the route, DLRs, errors, senders, and escalation are used. Technical observation records what occurred under defined test conditions.
These forms of evidence complement one another, but they are not interchangeable. A contract does not automatically prove the behaviour of every message. A DLR does not necessarily disclose the full supply chain. A limited test does not by itself establish a direct relationship. And a commercial statement does not replace documented operational restrictions.
The SMS specification includes success states, temporary errors, and permanent errors. However, DLR semantics exposed to customers may be transformed, normalised, or grouped by the provider. Therefore, the value of an observation depends on retaining its context, the semantics documented by the provider, and the received codes.
- Statement: what the provider claims and within what scope.
- Contract: what has been agreed and how changes are notified.
- Operational documentation: rules, codes, limits, and support.
- Technical observation: results recorded in a reproducible test.
Minimum Information Before Enabling a Route
Before sending production traffic, request an operational route record rather than only a commercial classification. The aim is for routing, quality, support, and compliance teams to understand what is permitted, how an incident should be interpreted, and who it should be escalated to.
The information should be linked to a specific version of the route. If a provider cannot disclose every detail of the chain, it should at least be able to indicate which part is not disclosed, which conditions it does confirm, and what the escalation procedure is when clarification is required.
- Immediate provider and entity responsible for the service.
- Destination country, scope range, and destination network where known.
- Declared classification: direct, hub, intermediated, or another agreed definition.
- Authorised traffic types and applicable exclusions.
- Sender ID rules, including preregistration, replacement, blocking, or known restrictions.
- Content, volume, time window, campaign, or use-case restrictions.
- Applicable limits and expected behaviour when they are exceeded.
- Response matrix, error codes, and DLR semantics supplied by the provider.
How to Record Intermediaries Without Exposing Sensitive Information
Intermediary records should be proportionate to their purpose. Where required by contract, regulatory requirements, anti-fraud controls, sanctions, audit, or risk management, the legal or commercial identity may be required. Where such disclosure is not needed for daily operations and does not conflict with applicable obligations, a stable pseudonymised identifier or functional category may be sufficient.
The important point is to retain disclosure traceability: which part of the chain is known, who knows the full identity, under which agreement it may be consulted, and what evidence supports the declared relationship. This makes it possible to manage confidentiality without turning a disclosure limitation into a claim of certainty.
Do not attempt to compensate for missing commercial detail with inferences based on latency, DLRs, or prefixes. These signals may be useful for observing behaviour, but they do not replace declared information.
- Use full identity where required by contract, regulation, anti-fraud controls, sanctions, audit, or risk management.
- Use stable pseudonymised identifiers for operational references where applicable obligations allow it.
- Record the intermediary's role where known.
- Note who is responsible for holding the full identity and the access conditions.
- Explicitly mark unverified or undisclosed segments.
Onboarding Questions That Test Whether a Route Is Operable
Onboarding questions should verify that a declaration can be turned into repeatable operations. Request documented answers with an owner and an effective date. Ambiguous responses should result in a condition, limitation, or exception; they should not be closed with a commercial label.
It is also advisable to verify consistency between the provider's documentation and its technical interfaces. If proprietary codes, generic DLRs, or state transformations are received, request their semantics and update criteria.
- Which destinations and networks does this declaration cover exactly?
- Which traffic types are permitted, and which are excluded?
- Which Sender ID rules apply, and how is a change communicated?
- Which acceptance, error, and DLR codes are delivered, including provider-specific codes?
- Which limits, time windows, or other operational restrictions are currently in force?
- Which NOC contact handles incidents, and what is the escalation chain?
- Which changes require prior notice, and how is that notice distributed?
- What test evidence can be provided with configuration, date, destination, and result?
How to Link Provenance and Testing Without Overinterpreting Results
Testing should be used to observe behaviour, not to claim certainty about the entire chain. For every test message, retain a test identifier, send time, destination, sender used, acceptance response, raw DLR, normalised DLR, timestamps, errors, and relevant configuration.
Observations may include DLR consistency, latency, availability, and Sender ID or content behaviour. They should be repeated whenever a relevant condition changes: destination, known network, traffic type, sender, configuration, immediate provider, or applicable restriction.
A DLR requires careful interpretation. Depending on its semantics, it may reflect different service states. It must not be presented as universal certainty that a person has read the message or, without reviewing the specific status and applicable documentation, as a guarantee of receipt on the handset. The absence of a DLR, a generic DLR, or an undocumented code is an observability limitation, not conclusive proof of origin or final outcome.
Latency and availability also depend on store-and-forward conditions, congestion, retries, and other operational factors. Therefore, neither low latency nor a DLR pattern can prove that a route is direct or that no intermediaries exist.
- Document the complete context of every test.
- Retain the raw DLR together with its internal normalisation.
- Compare the received DLR with the documented semantics.
- Test Sender ID by destination and use case; do not assume consistency across markets.
- Do not use isolated tests as proof of commercial or technical provenance.
Frequently asked questions
Does a route declared as direct guarantee SMS delivery?
No. The label must be understood within a documented scope. It does not replace destination restrictions, filtering policies, operational limits, or technical observation. It also does not guarantee receipt or reading by the end user.
Can a telephone prefix prove the applicable terminating network?
Not on its own. An E.164 number provides addressing structure, but portability and national conditions prevent a prefix from being used as standalone proof of the current terminating network.
Does a DLR prove that the message reached the handset?
It depends on the status semantics and applicable documentation. A DLR does not prove that a person read the message and should not be presented as a universal guarantee of handset receipt.
What should you do if the provider does not disclose all intermediaries?
Record which part of the chain is not disclosed, what evidence does exist, and who may access the complete information under which agreement. Then explicitly decide whether to approve it with conditions, limit the route to testing or non-critical traffic, or reject it.
When should a route provenance record be reviewed?
It should be reviewed on the defined date or condition and whenever the immediate provider, an identified intermediary, coverage, permitted traffic, Sender ID rules, limits, or DLR semantics change.
Sources consulted
- ITU-T Recommendation E.164 (02/2026): The international public telecommunication numbering planInternational Telecommunication Union (ITU)
- ITU National Numbering PlansInternational Telecommunication Union (ITU)
- E.164 Supplement 2: Number portabilityInternational Telecommunication Union (ITU)
- TS 123 040: Technical realization of the Short Message Service (SMS), 3GPP TS 23.040 v19.0.0ETSI / 3GPP
- TS 123 040: Technical realization of the Short Message Service (SMS), status-report semanticsETSI / 3GPP
- IR.75 Open Connectivity SMS Hubbing Architecture v2.0GSMA
- SG.22 SMS Firewall Best Practices and PoliciesGSMA
- Interworking Security knowledge baseGSMA