Validating A2P SMS Bulk Upload Files: An Operational Guide
A guide to designing staged checks for A2P SMS files, identifying fixable errors, and maintaining traceability without confusing validation with consent or delivery.
Problems Prevented by Validating Before Creating Messages
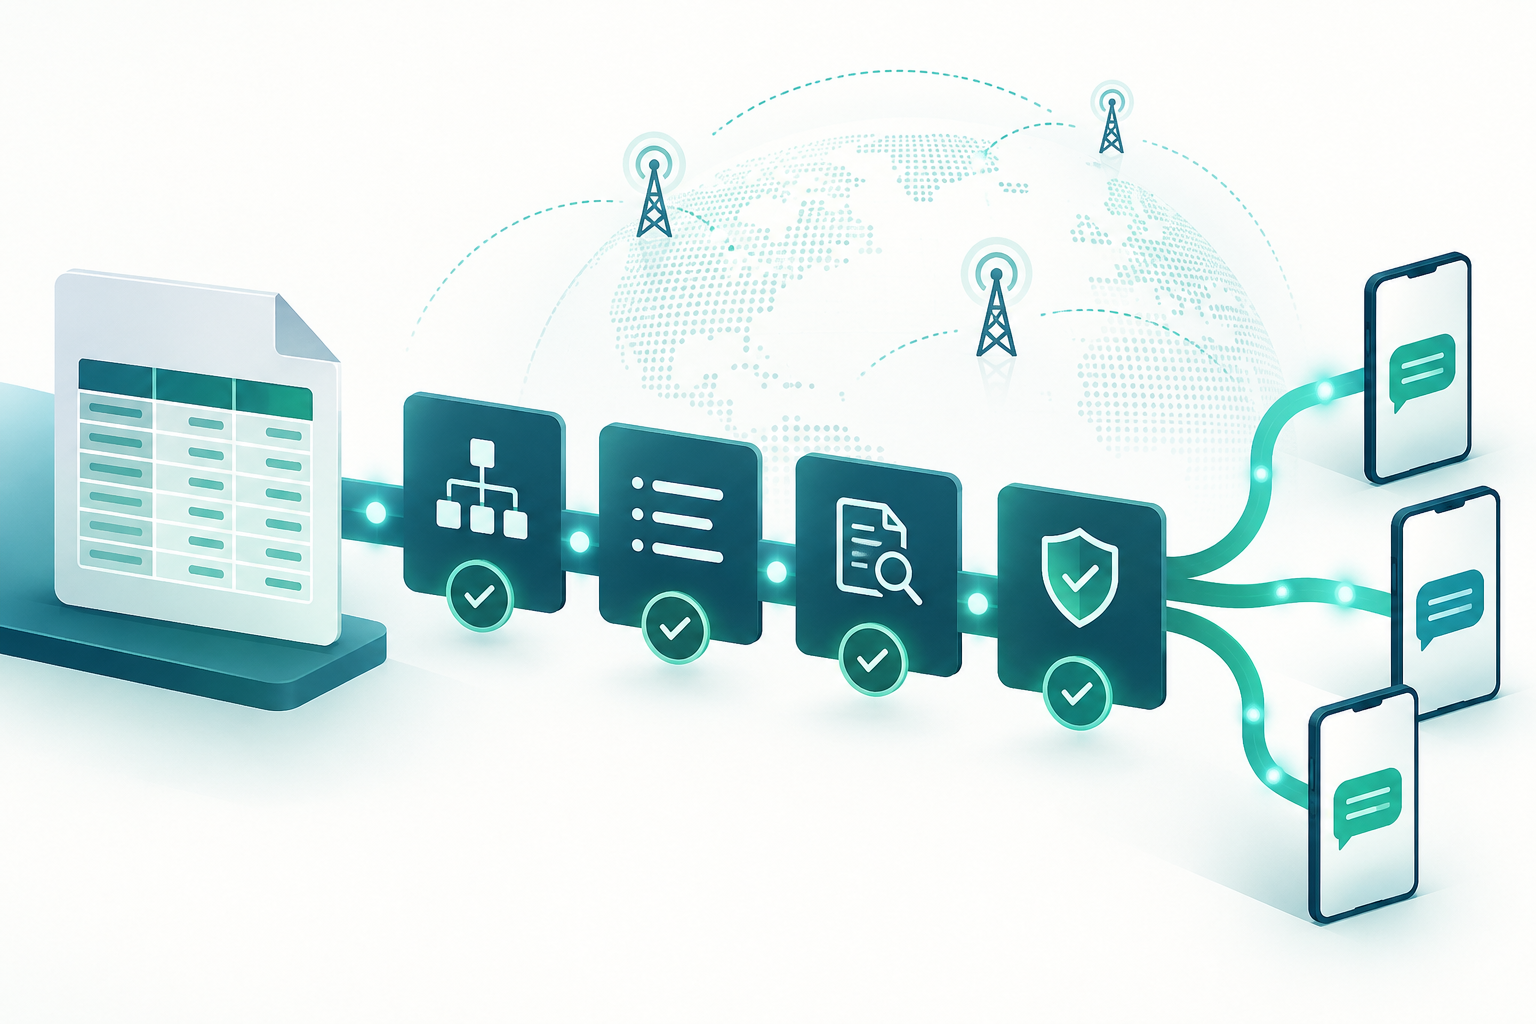
A bulk upload may contain correct data, incomplete records, and errors that make a row impossible to interpret. Validating before creating messages helps identify these problems in a controlled stage and show which records need review, rather than uncovering them after processing has begun.
Validation should be understood as a check of data and predefined rules. It does not prove that consent to contact exists, that a sender is authorized in a destination, or that a message will be delivered. Those checks belong to separate processes and depend on the context, applicable rules, and available capabilities.
- Agree on the structure the system accepts and the meaning of each field.
- Separate parsing errors from failures to meet operational rules.
- Maintain an unambiguous link between each original record and its result.
Define the Data Contract
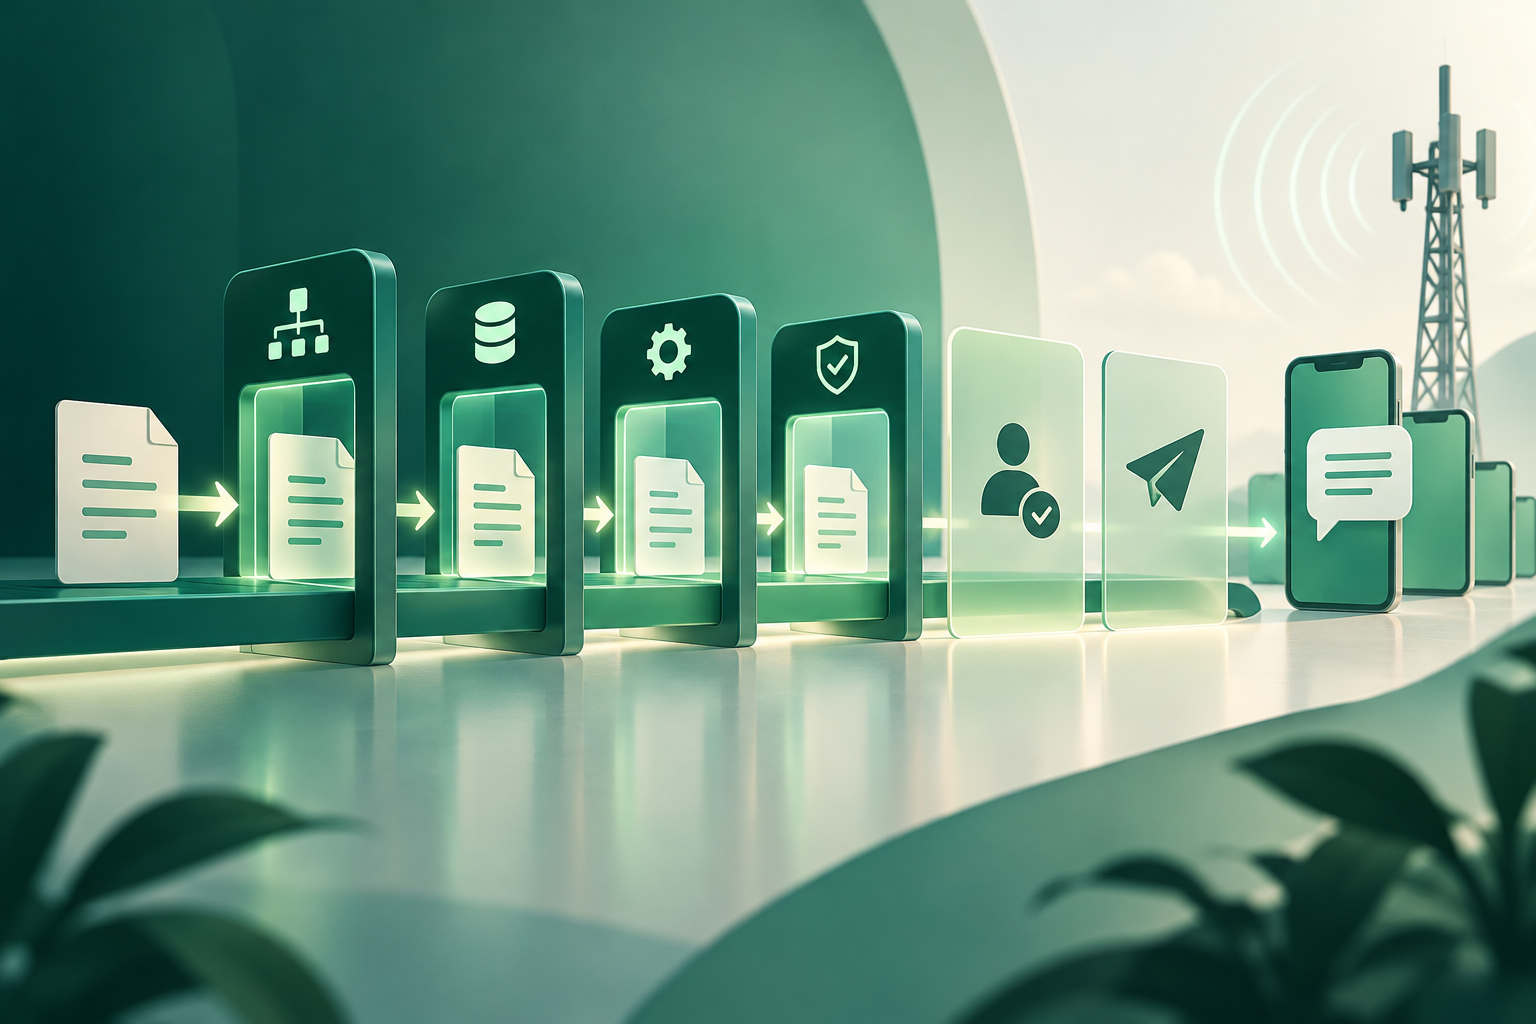
Before accepting files, document a data contract: supported formats, expected encoding, recognized headers, required fields, and how empty values are handled. If variants are accepted, specify them explicitly. Do not rely on assumptions such as column order or automatic interpretation of dates and numbers.
When reading a file, check that it can be interpreted using the declared format and that the required columns are present. Distinguish a file that cannot be parsed from one that can be read but contains incomplete rows. The first situation affects the whole file; the second can usually be reported per record.
The available evidence does not establish a single convention for encoding, headers, or required fields across all A2P bulk uploads. These rules should therefore be defined for each integration and communicated to the people preparing the files.
- Publish a template and a definition for each column, including formats and permitted values.
- State whether extra columns, empty fields, or alternative headers are allowed.
- Use different errors for an unreadable file, a missing header, and an empty required value.
Record-Level Checks: Number, Sender, and Content
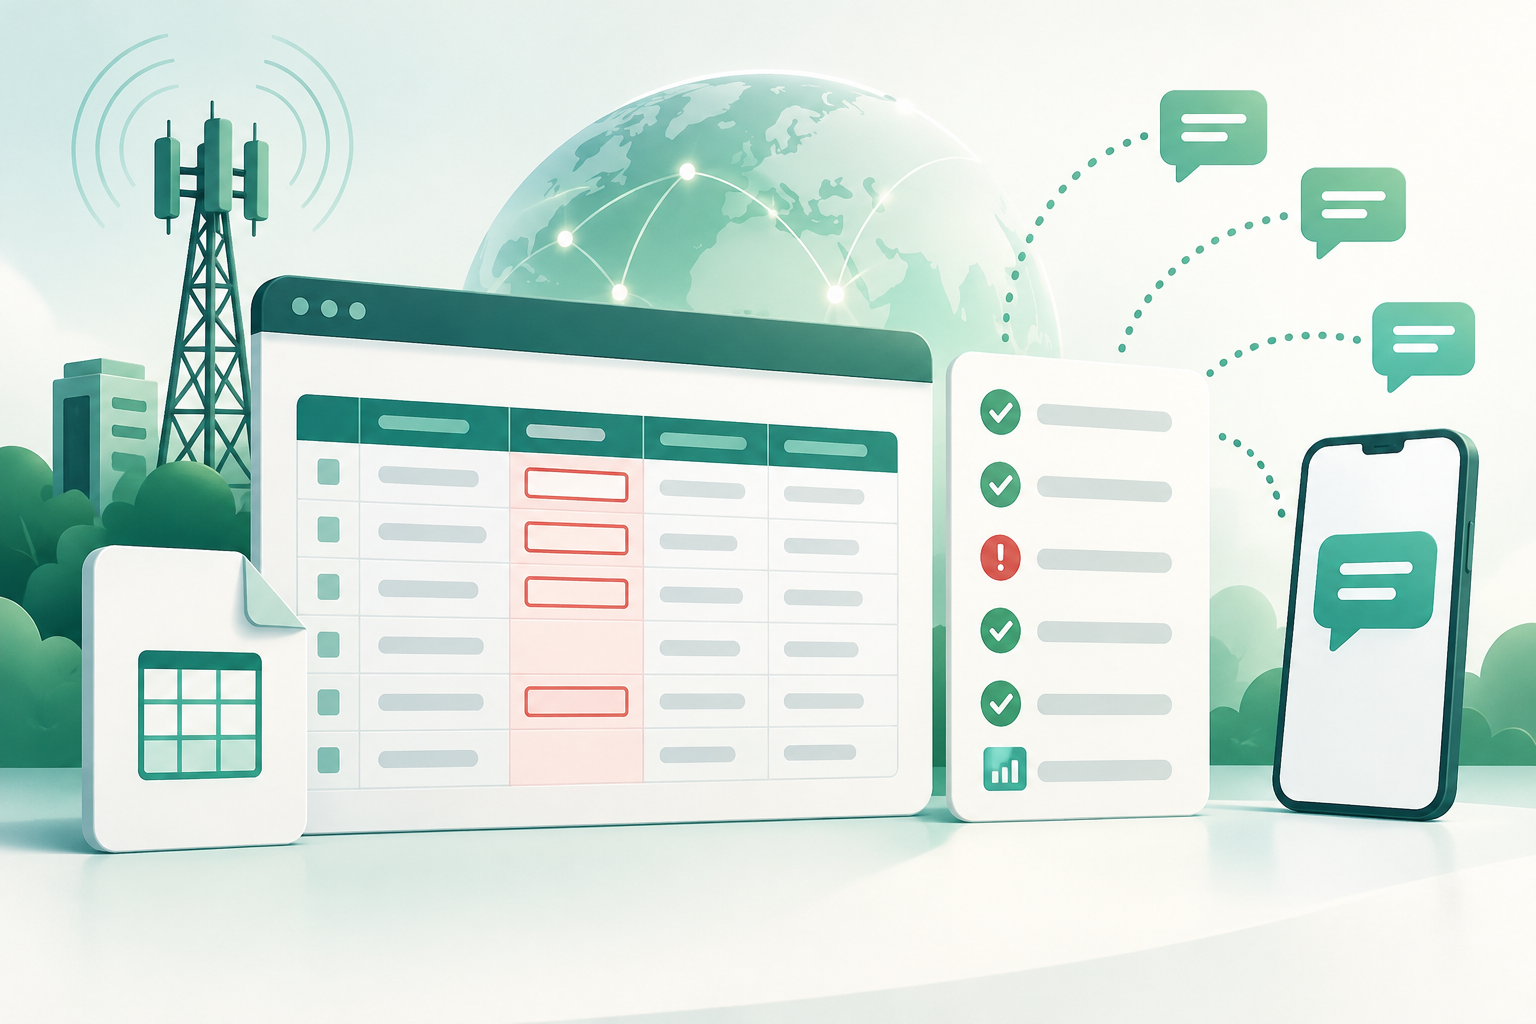
For each row, validate that the recipient number is present and can be interpreted according to the rules agreed for the integration. If normalization is applied, define and document its behavior; do not add prefixes, remove characters, or change the interpretation based on an assumption. E.164 is a reference for international numbering, but the information available here does not support detailing its rules or concluding that a string that follows them is routable.
Check that the sender and content are present when required by the use case and can be represented in the expected format. A sender's valid syntax does not prove that it is authorized for the destination. Likewise, readable text does not confirm that it meets consent requirements, applicable policies, or route restrictions.
Keep data checks and sending decisions separate. A row can be syntactically valid and still require an authorization, policy, or eligibility review before processing.
- Define the supported number formats and which cases are rejected or require review.
- Validate the sender against the rules configured for the context, without treating syntactic validation as authorization.
- Check that the content can be interpreted and that required personalization fields are available.
Detect Duplicates Without Changing the Intent
Two similar rows are not necessarily duplicates: they may represent legitimate messages to the same person, for example, at different times or for different purposes. Before flagging duplicates, define which combination of fields—and what time period, if any—will be used to detect matches. Do not automatically delete or combine records without a rule agreed with the process owner.
It is useful to distinguish an exact duplicate within the file, a match according to a business rule, and a legitimate repeat. The decision may be to warn, block, or allow the record through; it should be explicit, auditable, and consistent with the purpose of the message.
- Define the comparison key and detection scope before implementation.
- Preserve the original records and report which rows match.
- Do not present a match as proof of error or fraud.
Classify Errors by Stage
A useful classification separates at least three levels. Format errors prevent the file from being read or a field from being interpreted. Business-rule errors indicate that a value does not meet an agreed condition. Sending restrictions cover later decisions about authorization, policies, or whether the traffic can be processed. Do not combine these categories into a single generic “invalid” status.
A fixable error can be resolved by changing the file or data and validating it again. Under the configured rules, a definitive rejection means that the record must not proceed in that process. Avoid calling an error definitive if it only means that information or review is missing. Classification should reflect the known cause, not a conclusion the check cannot establish.
- Use distinct statuses for an unreadable file, fixable data issue, unmet rule, and pending review.
- Explain what action the person preparing the upload can take.
- Do not turn a validation failure into a claim about consent, identity, or delivery.
Actionable Results and Row References
Each validation result should identify the record that was checked and the reason for a warning or rejection. To do this, maintain a stable reference to the source record, such as its row number in the received file and, if available, an upload-specific identifier. The reference should remain intact even if the system transforms or normalizes values for processing.
Describe the affected field, the rule applied, and a possible action. Avoid ambiguous messages such as “number error” when you can say that the recipient is missing or the value does not meet the expected format. The returned information should be sufficient for correction without exposing unnecessary personal data.
- Include the upload ID, row reference, field, result, and a clear reason.
- Distinguish warnings from rejections and explain what to do next.
- Protect personal data in reports, logs, and support channels.
Large Uploads, Batches, and Resubmissions
The maximum file size, number of records per batch, and processing strategy depend on the system receiving the upload. There is no evidence here to support universal numerical limits. Set limits based on the implementation’s verified capabilities and publish them before teams prepare their files.
If processing occurs in batches, preserve the upload ID and each row’s position through every stage. Design resubmissions so that a partial failure does not silently turn a repeat into new messages. Retry and deduplication semantics must be specified by the integration; they cannot be inferred solely from the fact that the file was submitted again.
- Document limits and behaviors verified for the specific integration.
- Record which parts were validated and processed without hiding partial results.
- Define how a repeat upload is recognized before allowing resubmissions.
Traceability and Proportionate Retention
Maintain a verifiable link between the received file, each row, the validation result, and any message that is eventually created. This traceability helps investigate errors and answer operational questions, but should be limited to the data necessary for the defined purpose.
Establish a retention policy for files and results that specifies who can access them, what data is kept, and when it is deleted. The available information does not determine an appropriate retention period or replace obligations that apply in each jurisdiction. Define these limits with the people responsible for privacy, security, and compliance, and avoid keeping complete copies when a minimal reference is sufficient.
- Keep upload and row identifiers that make it possible to reconstruct results without unnecessarily duplicating data.
- Restrict access and avoid including full numbers or messages in logs unless necessary.
- Set retention periods according to the purpose and applicable obligations.
Frequently asked questions
Does a validated file prove that recipients gave their consent?
No. Structure and data validation only show that the upload meets the configured checks. Consent and other messaging obligations require separate checks.
Does a number that passes validation guarantee that the SMS will arrive?
No. A format check does not prove that the number is active, that a route is available, or that the message will be delivered. It should not be presented as a delivery guarantee.
Should duplicate rows be deleted automatically?
Not without an agreed rule. Similar matches may correspond to legitimate messages. Define how duplicates are identified and whether they are warned about, blocked, or allowed.
What information should a validation error include?
At a minimum, it should include a reference to the upload and row, the affected field, the reason, and a possible action. Limit the personal data exposed in the report.
What should the maximum file size be?
It depends on the verified capabilities of the system and integration. Define and communicate the specific limit; there is no universal value that can be recommended here.
Sources consulted
- Especificación SMPP v3.4SMPP Developers Forum
- Recomendación E.164Unión Internacional de Telecomunicaciones (ITU-T)
- Especificaciones 3GPP3GPP
- Semántica HTTP (RFC 9110)IETF