HTTP Rejections in A2P SMS: How to Separate Integration Errors from Delivery Failures
An HTTP response describes one stage of an integration, not necessarily the final SMS outcome. Learn how to record evidence, classify issues, and decide when to fix, retry, or escalate.
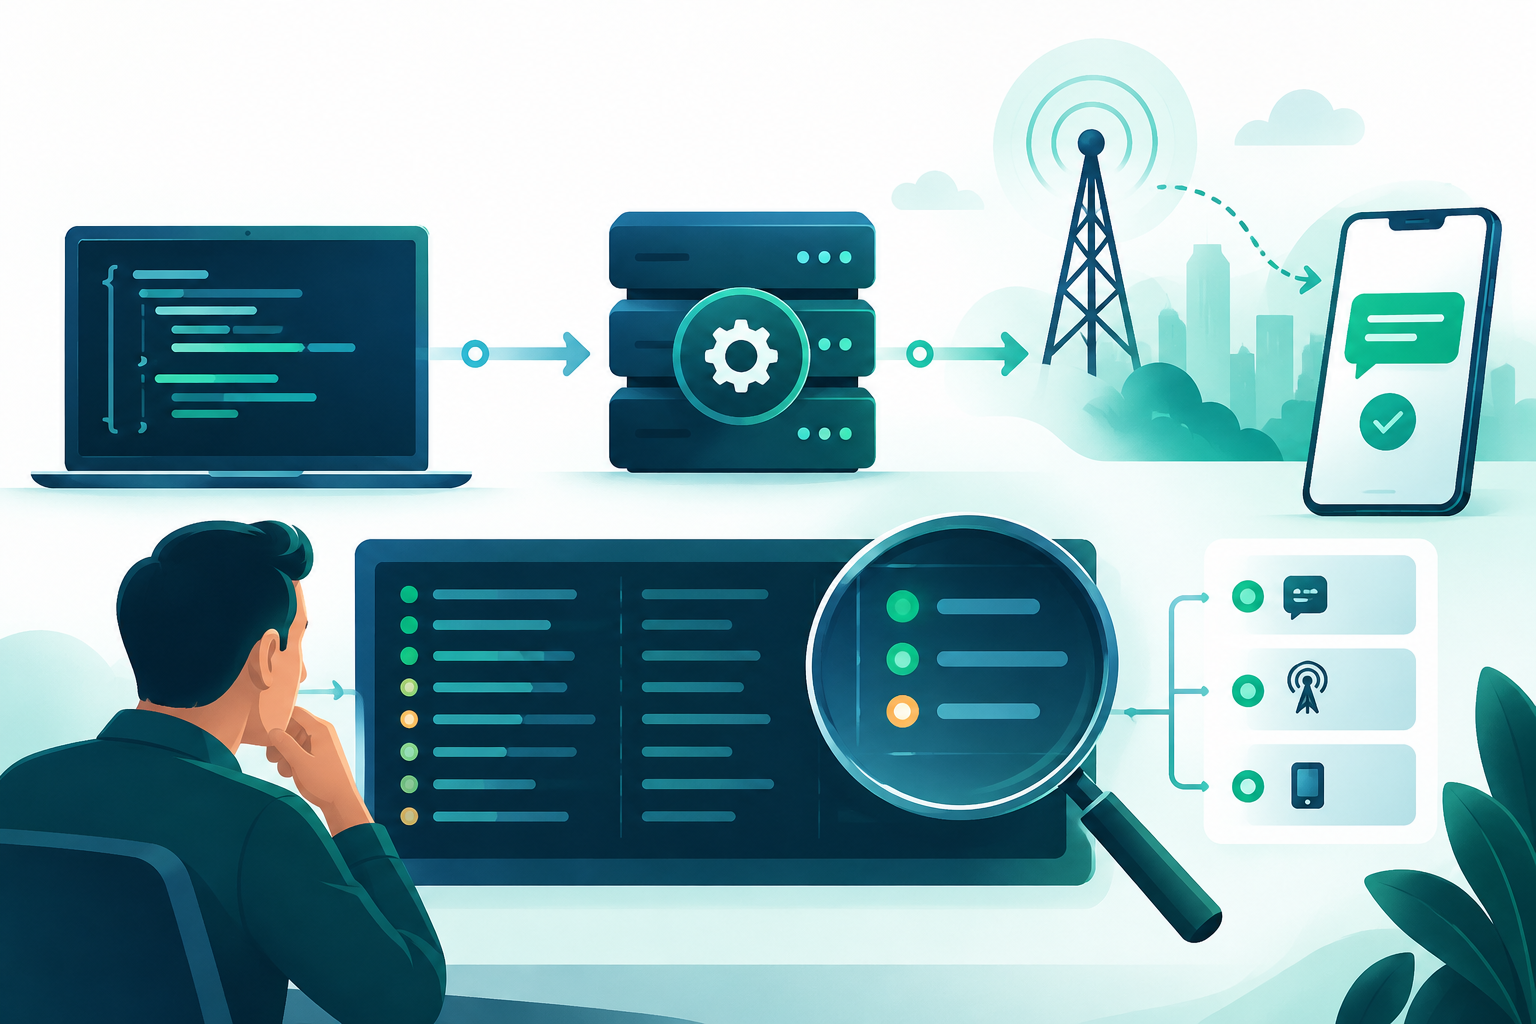
What an HTTP response means—and what it doesn’t
An HTTP response reports the result of the exchange between the client and the endpoint according to the API implementation. By itself, it does not confirm that the provider accepted the SMS for processing or that the message reached the phone.
In an SMS integration, distinguish three outcomes: the HTTP transport response, the API’s acceptance or rejection of the send request, and the message’s subsequent status. In SMPP, for example, delivery reports may be communicated through deliver_sm or data_sm messages; these are mechanisms separate from the initial HTTP response.
The meaning of each response depends on the API contract. Consult the provider’s official documentation to determine what the HTTP code indicates, what the response body confirms, and how to obtain the message’s subsequent status.
Separate the stages before diagnosing
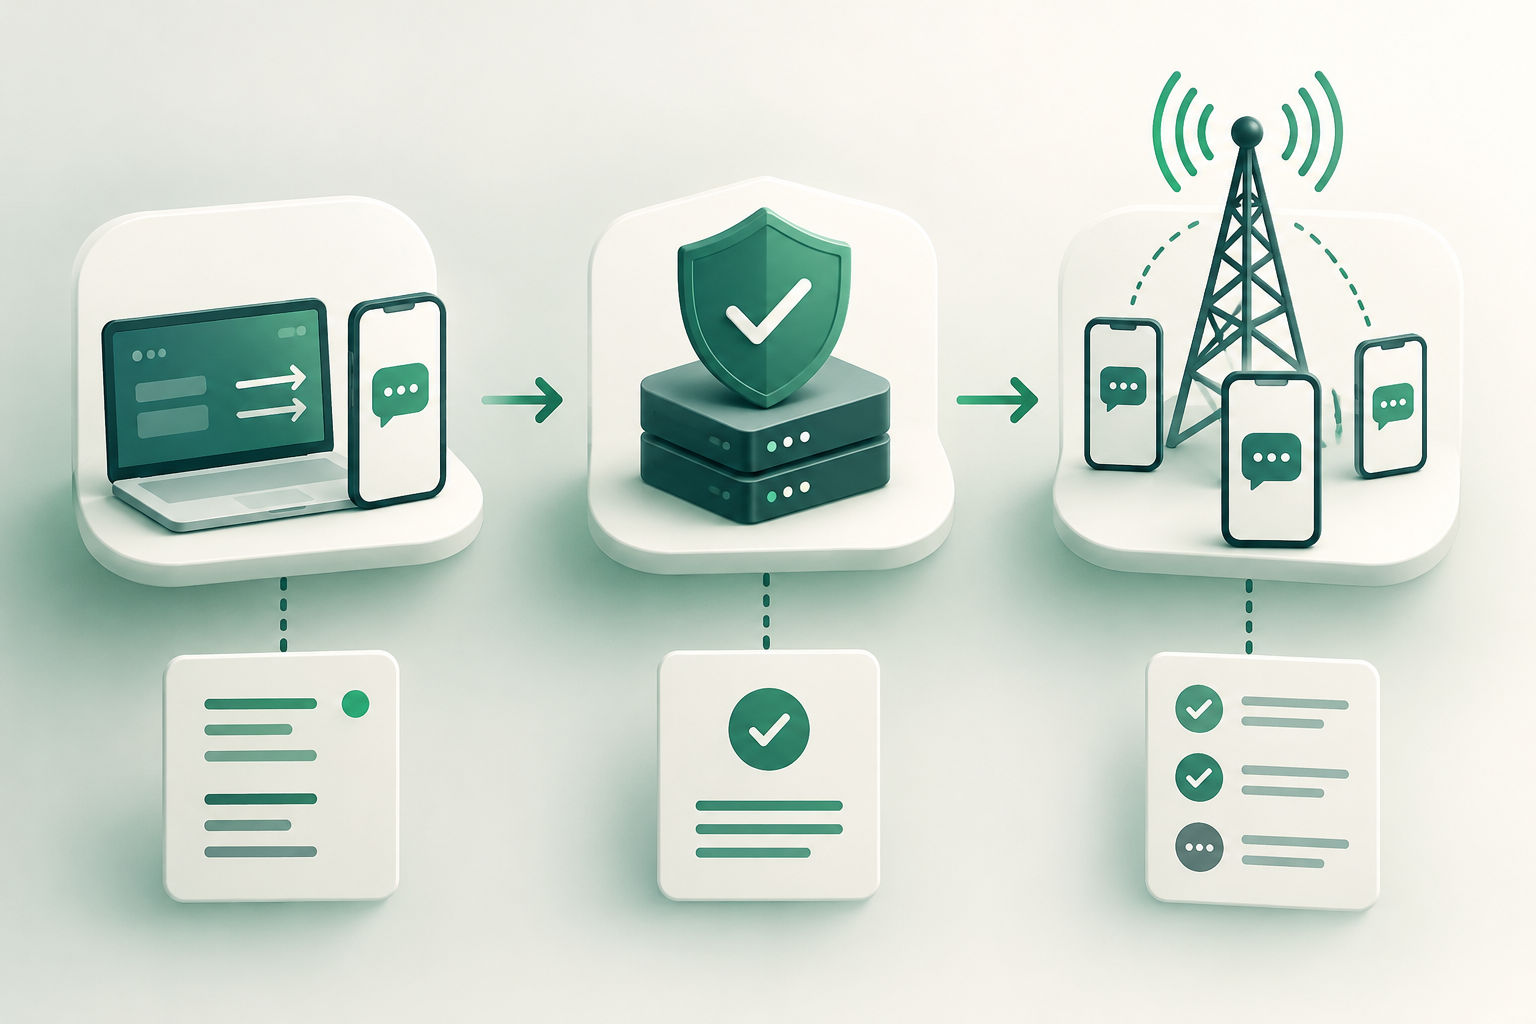
Model the journey as observable stages, not as a single “sent” or “failed” result. This separation helps prevent attributing an authentication issue to the mobile network or treating technical acceptance as confirmed delivery.
HTTP transport: determine whether your client could communicate with the endpoint and what response it received. A connection failure or timeout does not prove that the API failed to process the request.
Validation and acceptance: review the API response according to its documentation. It may indicate that a request was invalid, rejected, or accepted for a subsequent stage; don’t assume that all providers use the same response structure or semantics.
Subsequent status: use the documented mechanism to find out the SMS’s progress or outcome, such as a delivery report when available. A DLR reported by the platform should not be described as independent verification that the message was received on the device.
Record the minimum context needed to reconstruct the case
Logging fields are not universal: the API contract and security policies determine what data is available and how long it is retained. As an operational baseline, capture the available elements that can link the request to its response and to any subsequent status.
Include the time and time zone, your system’s correlation ID, and the reference returned by the API, if one exists. Keep the method and endpoint used, the HTTP code, the relevant response body, and the integration version.
Record the destination in the normalized format you sent and the technical attributes needed to reproduce the request, such as sender type or encoding when these are part of the API. Avoid storing content or personal data that is not needed for diagnosis, and follow your organization’s access and retention rules.
Do not confuse your application’s internal ID with a provider message reference. Clearly note which system generated each identifier.
- Time and time zone of the attempt.
- Internal correlation ID and provider reference, if returned.
- Normalized destination, method, and endpoint; protect sensitive data.
- HTTP code, API response, and operation outcome according to the contract.
- Available subsequent status and the time it was observed.
Classify the issue by stage and evidence
Don’t turn a generic code table into a definitive diagnosis. HTTP ranges provide context about the server response, but the cause and appropriate action must be checked against the API documentation and the response body.
Connectivity: if there is no HTTP response, check endpoint resolution, the connection from the sending environment, timeouts, and the logs available at both ends. No response does not prove that the server did not receive the request.
Authentication and authorization: if the response or body points to credentials or permissions, verify the authentication method, environment, and configured permissions. Don’t include secrets in tickets or shared logs.
Format and validation: if the API rejects parameters, compare the request with the official schema, including required fields, destination format, and documented restrictions. Correct the request before sending it again.
Limits or policies: if the documentation or response identifies a limit, quota, or restriction, confirm its scope with the provider. Don’t infer an allowed rate from a single response.
- First identify where the evidence appears: transport, validation, acceptance, or subsequent status.
- Interpret the HTTP code and response body together, not in isolation.
- Record which conclusions are confirmed and which remain hypotheses.
Timeout: an uncertain outcome, not a confirmed rejection
If the client times out, it may not know whether the request reached the server or whether the server processed it before the response was lost. Without documented idempotency semantics, resending could create a second attempt and potentially a duplicate message.
Before retrying, look for a reference or status lookup documented by the API for that operation. Check the sender’s logs and, if possible, ask the provider to verify whether it received the original request. Don’t invent an idempotency key or assume that repeating the call is harmless.
- No response and no evidence of receipt: classify the outcome as unknown, not as a proven rejection.
- Explicit rejection, interpreted according to the documentation: correct the cause before trying again.
- Acceptance confirmed but no subsequent status: investigate the status lookup or reporting mechanism before sending again.
A reproducible diagnostic procedure
Work with an authorized, controlled case and follow applicable consent and traffic rules. The goal is to isolate the failing stage, not to increase volume or test unauthorized destinations.
1. Preserve the observed request and response, protecting credentials and personal data. Check that the client is not discarding the HTTP code or replacing the response with a generic message.
2. Consult the contract and official documentation for the API version in use. Confirm the meaning of the code, response fields, message references, status mechanism, and any documented retry and idempotency rules.
3. Compare the actual request with a valid request under the published schema. Change one variable at a time and reproduce only through an authorized workflow.
4. Correlate the time and identifiers with the sender’s and provider’s logs. Distinguish observed facts from inferences—for example, “HTTP response received” versus “message accepted” or “DLR received.”
Decide whether to fix, retry, or escalate
Fix the integration when the evidence and documentation point to incorrect credentials, permissions, formatting, or parameters. Don’t escalate an issue as a delivery failure when it has not yet passed API validation.
Retry only when the API contract and evidence establish that it is safe. If the operation may have been processed and there is no documented protection against duplicates, first resolve the uncertainty using the reference, a status lookup, or the provider’s support team.
Escalate when the issue persists with a compliant, authorized request, or when the evidence places the incident in the provider’s service or a subsequent stage under the provider’s responsibility. Share the time, time zone, identifiers, endpoint, HTTP code, and relevant response; redact secrets and limit recipient data to what is necessary.
- Fix: rejection attributable to a request or configuration you can verify.
- Retry: only under a documented rule and without duplicating an uncertain outcome.
- Escalate: provide correlatable evidence that locates the incident outside the sender’s integration.
What not to infer from a 2xx, an error, or a missing DLR
An HTTP 2xx does not automatically confirm SMS delivery: it may indicate a successful HTTP outcome whose exact scope is defined by the API. Check whether the body confirms acceptance and how subsequent statuses are reported.
An HTTP error response does not, on its own, identify the ultimate cause. It may relate to transport, authentication, validation, or another condition specific to the implementation; use the response and official documentation.
A missing DLR does not, by itself, prove either delivery or failure. Determine whether the report is available, what it means in that service, and whether there is enough information to associate it with the message. Always distinguish a status reported by the platform from independent confirmation that the device received the message.
Frequently asked questions
Does HTTP 200 mean the SMS was delivered?
Not necessarily. An HTTP response describes the exchange with the API. Send acceptance and subsequent statuses are separate stages; confirm what they mean in the provider’s official documentation.
Should I resend the SMS if the call times out?
Not automatically. The outcome may be uncertain: the server may have received or processed the request even though the client did not get a response. Check the documented reference or status and verify the retry and idempotency rules before resending.
What information should I send to the provider’s support team?
Share the time and time zone, available correlation identifiers, endpoint, HTTP code, relevant response, and the affected stage. Protect credentials and minimize personal data.
Does a missing DLR prove that the message was not delivered?
No. A missing report does not, by itself, confirm either delivery or failure. Check the provider’s reporting mechanism and documented statuses; a reported DLR is also not independent verification that the device received the message.
Sources consulted
- HTTP Semantics (RFC 9110)IETF
- SMPP v3.4 SpecificationSMPP Developers Forum
- Comprender los mensajes rechazadosSinch Support
- Preguntas frecuentes de la API SMSAltiria