A2P SMS Suppression List Synchronization: An Operational Guide
How to design the propagation and verification of opt-outs and restrictions across CRMs, campaign platforms, and sending systems—without confusing consent with delivery.
Why suppression lists fall out of sync
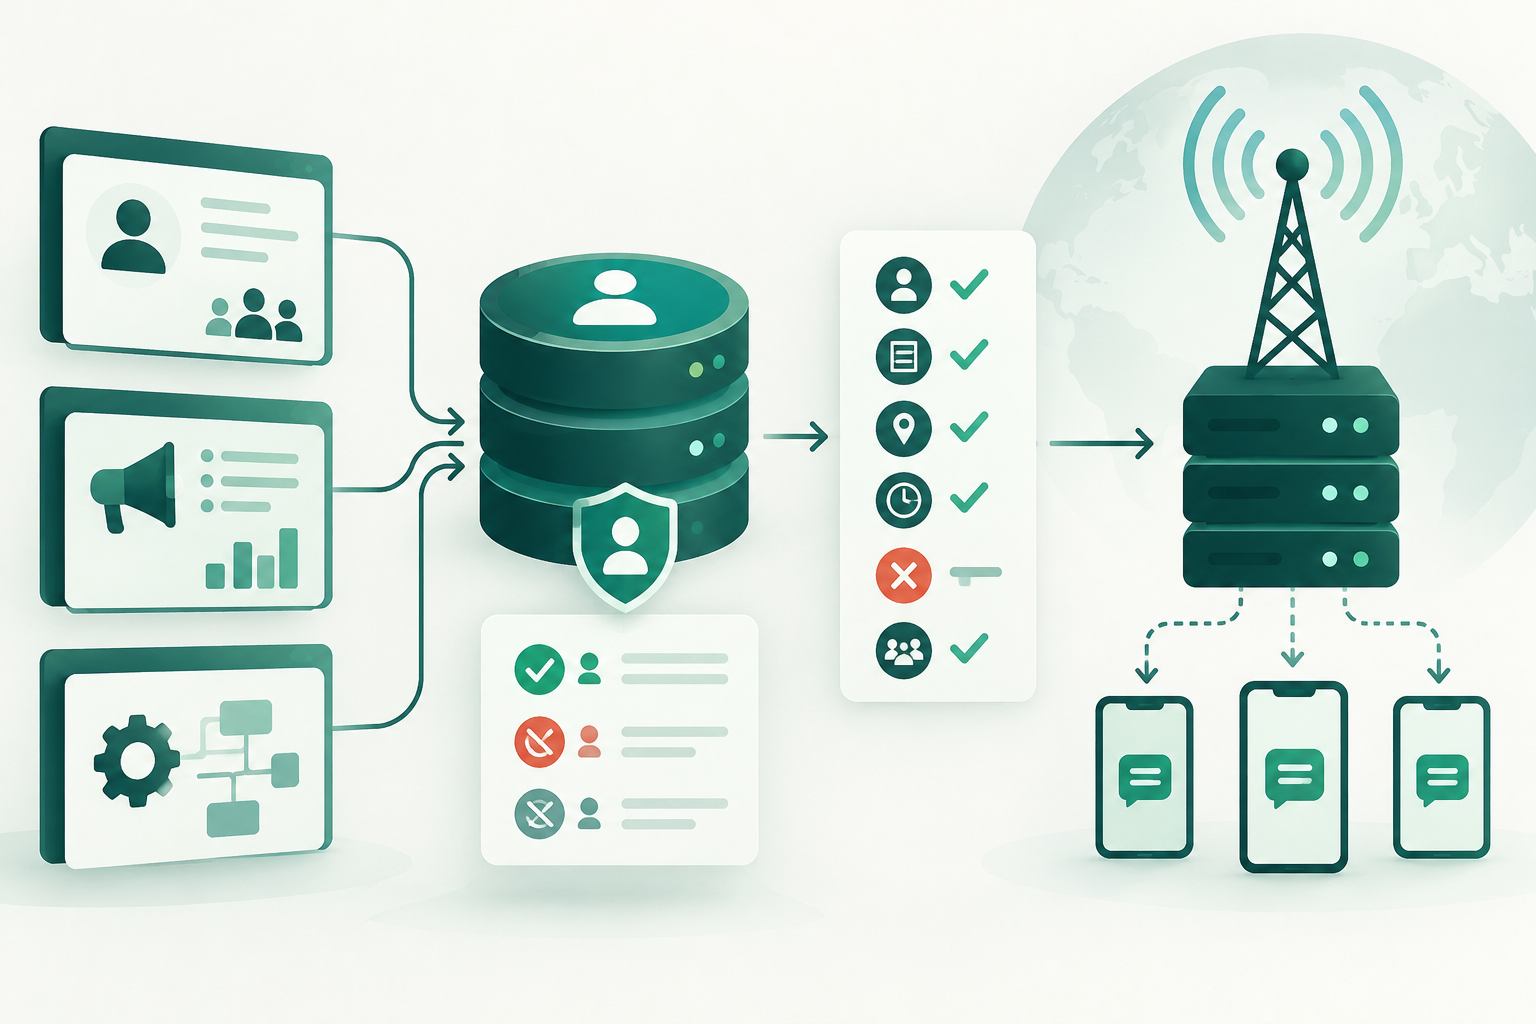
In an architecture with a CRM, a campaign tool, and one or more sending layers, each system may keep a different copy of preferences. An opt-out received through one channel may take time to reach the others. It may also fail to propagate if the integration only syncs opt-ins or if a task fails without generating a visible alert.
Consent synchronization across applications is an explicit function, not an automatic consequence of connecting systems. Available documentation on consent synchronization confirms the general goal of applying decisions across multiple applications, but it does not define a universal design for A2P SMS suppression. The workflow therefore needs to be defined and tested for the specific architecture.
- List every system that receives, changes, or checks preferences and restrictions.
- Identify the events that can trigger an opt-out or a change in eligibility.
- Check which fields sync automatically and which require a rule or manual intervention.
- Do not assume a change has propagated just because the source system confirms that it saved the change.
Separate the sources of truth
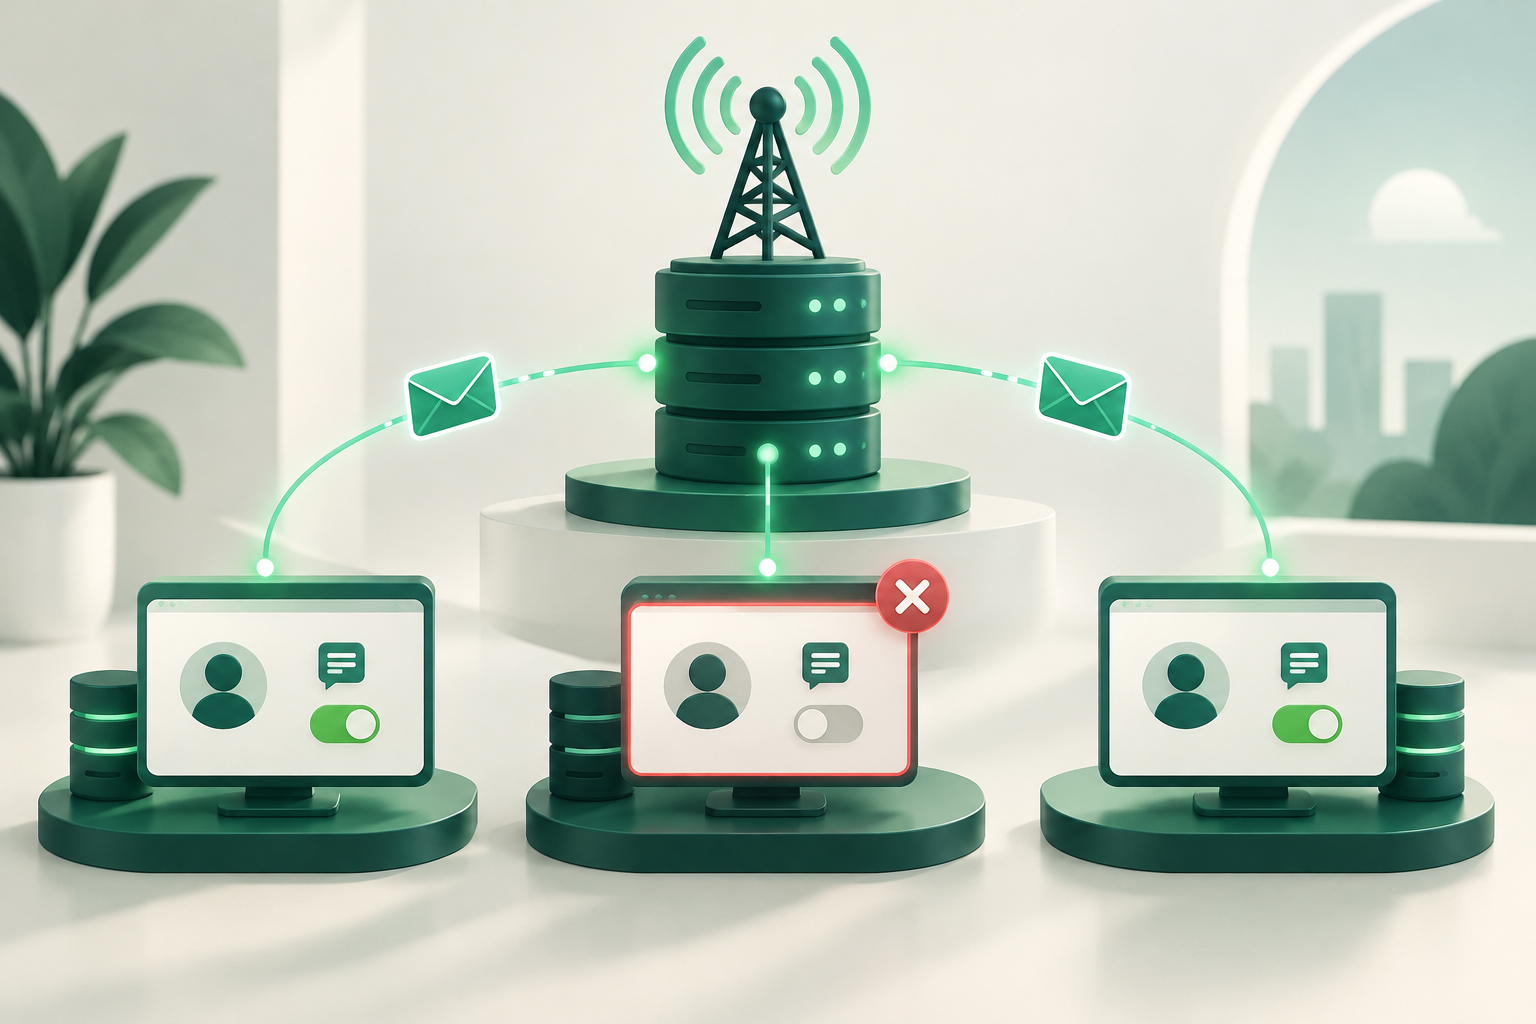
Consent, eligibility, and sending status should not be treated as a single data point. Consent and eligibility are business decisions that must be determined by the responsible systems and applicable policies. A sending system may enforce an operational restriction, but the fact that it technically accepts a request does not prove that the contact is eligible to receive it.
Define an authoritative source for each type of information. For example, an organization may decide where a contact’s preference is recorded and where operational restrictions are checked. The design should specify how differences between records are resolved and which system is authoritative for each data point; there is no universally supported precedence rule for every case.
- Document who can create, change, and remove each type of restriction.
- Distinguish consent status from the technical result of a sending request.
- Set an approved rule for conflicts between systems before launching campaigns.
- If a discrepancy has no defined resolution, pause or hold the affected send until it is clarified.
Model changes with enough context
A useful change record should make it possible to determine which contact it refers to, what changed, and where the decision came from. In the implementation, define stable identifiers within your architecture, a timestamp, the type of change, and its source. Include the scope of the restriction when needed to distinguish, for example, preferences by purpose, brand, or channel.
Timestamps help reconstruct the sequence, but cannot resolve every conflict on their own: events may arrive late, clocks may be unsynchronized, or sources may differ. Add event identifiers and retain the information needed to trace processing, with appropriate access and retention controls.
- Associate each change with an organization-defined contact identifier and avoid relying solely on a text match.
- Record the change type, scope, source, and time received; distinguish this from the time reported by the source if both are relevant.
- Define how an opt-out, a temporary restriction, and a preference change are represented, without assuming they are equivalent.
- Limit recorded personal data to what is needed to operate, investigate discrepancies, and meet applicable obligations.
Handle duplicates, delays, and out-of-order events
Integrations should account for the possibility that the same event is received more than once or arrives after another change. Define how to recognize an event that has already been processed and prevent its repetition from producing new effects. Also establish an explicit rule for contradictory events; do not assume that the most recently received message always represents the current decision.
In particular, an old opt-in that arrives late should not automatically reactivate a contact if a later opt-out exists according to the authoritative source. The exact rule depends on the data model, consent scopes, and business policies. If precedence cannot be determined confidently, escalate the issue or keep the restriction in place while it is resolved.
- Assign each event a unique identity and record whether it has been processed.
- Compare the sequence with the authoritative source, not just the order in which events arrived.
- Test repeated, delayed, and contradictory events before using the workflow in production.
- Do not let an opt-in sync remove restrictions without a valid, traceable decision.
Propagate changes with processing tracking
A queue or equivalent mechanism can decouple the receipt of changes from their propagation, but having one does not, by itself, guarantee synchronization. The implementation should specify what it means for an event to be accepted, processed, and applied at each destination. A receipt confirmation does not necessarily confirm that the update was successfully applied.
Design controlled retries for temporary failures and a review path for errors that do not resolve automatically. Record persistent failures and alert the responsible people. General synchronization guidance highlights change planning and identifying information that cannot be synchronized automatically; specific retry and confirmation parameters must be decided and tested for each system.
- Define observable states for received, processing, applied, and failed, based on the actual capabilities of each integration.
- Ensure that repeating an operation does not remove or duplicate its intended effect.
- Set limits and alerts for retries, along with a queue or process for reviewing errors.
- Verify the applied status in the destination system when the integration allows it.
Check eligibility close to sending
A list checked when a campaign is created may be out of date before the messages are sent. Consider checking eligibility as close as possible to the point of sending, using the authoritative source or a representation whose freshness and limitations are known. The check should apply business decisions; the technical layer should not invent or reinterpret consent.
The architecture and available latency will determine how to implement this control. Do not assume that every campaign platform, API, or messaging connection supports a real-time check, or that a sending response validates consent. Document what is checked, which data version or timestamp is used, and what happens if the lookup service is unavailable.
- Validate eligibility before handing the message to the sending layer, where the architecture allows it.
- Define an explicit policy for stale data or failed lookups; do not leave it implicit in platform behavior.
- Keep the eligibility decision separate from the technical acceptance of a request.
- Test whether an opt-out received while a campaign is being prepared can be detected before pending messages are sent.
Reconcile records before and after campaigns
Reconciliation compares records across systems to find differences that the normal workflow did not detect. It can run periodically and before significant campaigns, with scope and frequency determined according to risk and operational capacity. The comparison should account for identifiers, scopes, and equivalent statuses; comparing fields with different meanings produces false matches.
Classify discrepancies, determine which source is authoritative for each field, and document how each issue is resolved. Reconciliation does not replace ongoing propagation or authorize automatically overwriting a conflicting record. First identify which data can be synchronized safely and which requires review.
- Compare a sample or the set defined by your procedure across the preferences source and relevant destinations.
- Detect missing contacts, differing statuses, unconfirmed events, and scope mismatches.
- Assign an owner, priority, and resolution to each discrepancy.
- Repeat the check after correcting errors and retain an operational summary of the results.
Test the workflow and retain proportionate evidence
Before deploying changes, test the full path from the origin of an opt-out to the systems that can initiate or accept a send. Include integration failures and recovery, as well as normal cases. Tests should confirm both the functional outcome and the ability to detect incomplete propagation.
Retain enough evidence to explain which change was received, how it was processed, and what check was performed, but do not accumulate personal data without a defined purpose. Apply internal access and retention policies, and have qualified personnel assess relevant legal obligations. This guide describes general operational controls; it does not replace legal advice or establish universal requirements.
- Test a normal opt-out, a duplicate event, a delayed event, a destination outage, and subsequent recovery.
- Verify that a restriction is not removed by an opt-in import or synchronization.
- Store event identifiers and processing results according to an approved retention policy.
- Review integration changes and fields that do not sync automatically whenever the architecture changes.
Frequently asked questions
Does an acceptance response from the sending system prove that the contact had consent?
No. Technical acceptance of a request and business eligibility are separate questions. The sending system’s response alone does not prove that consent is valid or current.
Should the most recent change always take precedence?
There is no universal rule for every architecture. Define which source is authoritative, how times and scopes are compared, and what to do when records conflict. If the decision cannot be determined with confidence, do not automatically reactivate the contact.
Does a single suppression list eliminate the need to reconcile systems?
Not necessarily. It may reduce duplication, but integrated systems can still have delays, failures, or fields that do not sync automatically. Check propagation and periodically compare relevant statuses.
Does this guide set legal requirements for every A2P SMS send?
No. Rules depend on the jurisdiction, purpose, and context of the message. Use this guide as an operational reference and consult qualified legal counsel to determine the applicable requirements.
Sources consulted
- Sincronizar el consentimiento en varias aplicacionesGoogle Ad Manager Help
- Consejos adicionales para la sincronizaciónIBM Documentation
- Gestionar el mensaje de consentimiento SMS en los formulariosActiveCampaign Help
- Uso de la lista de supresión de nivel de cuenta de Amazon SESAmazon Web Services Documentation