Consent and Suppression Lists in A2P SMS: An Operational Guide
Learn how to demonstrate the scope of consent, apply opt-outs across all routes, and block messages before they are queued—without confusing authorization with deliverability.
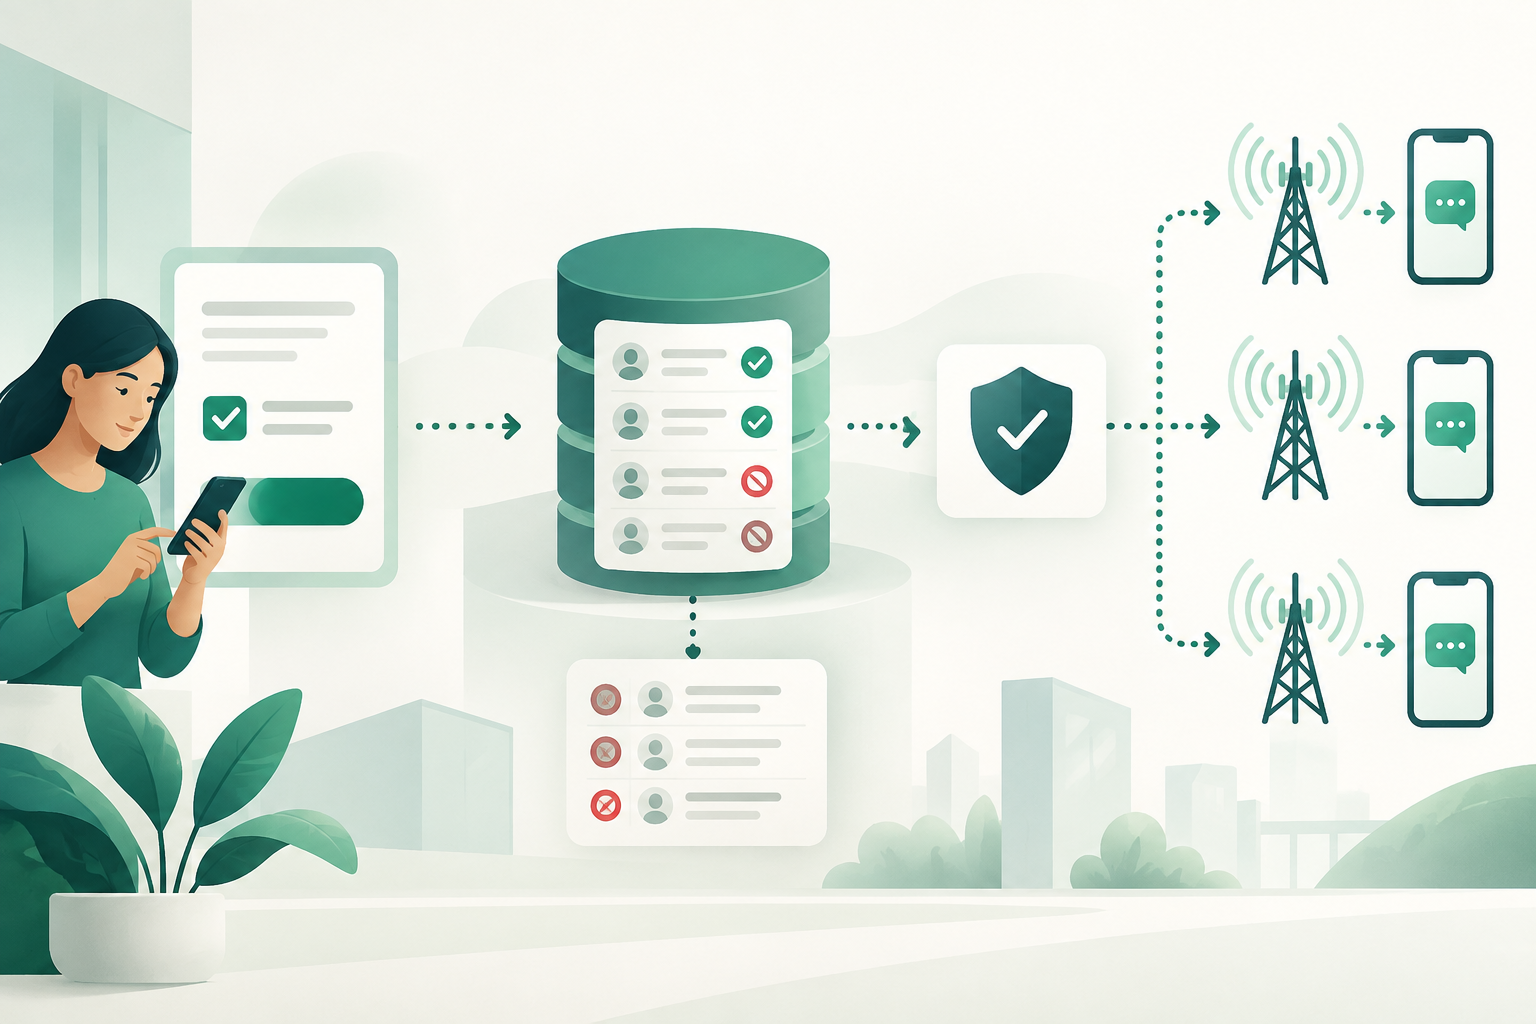
Consent, eligibility, and delivery are separate controls
A platform accepting a message, or a route being able to carry it, does not prove that the recipient authorized that message. Authorization must cover the relevant purpose, campaign, and sender; eligibility determines whether sending remains permitted under current preferences and restrictions. Delivery, in turn, is a separate technical outcome.
Design the send decision as a pre-send control: check that a valid basis exists for the purpose, that no applicable opt-out is on record, and that the combination of brand, channel, and jurisdiction is permitted. This is operational guidance, not a universal legal formula. Review the rules applicable to each market and message type.
- Do not treat a favorable response from a route as proof of consent.
- Do not treat consent for one campaign, sender, or subject as authorization that transfers to others.
- Do not confuse a technical send confirmation or DLR with proof of authorization or independent verification that the message reached the device.
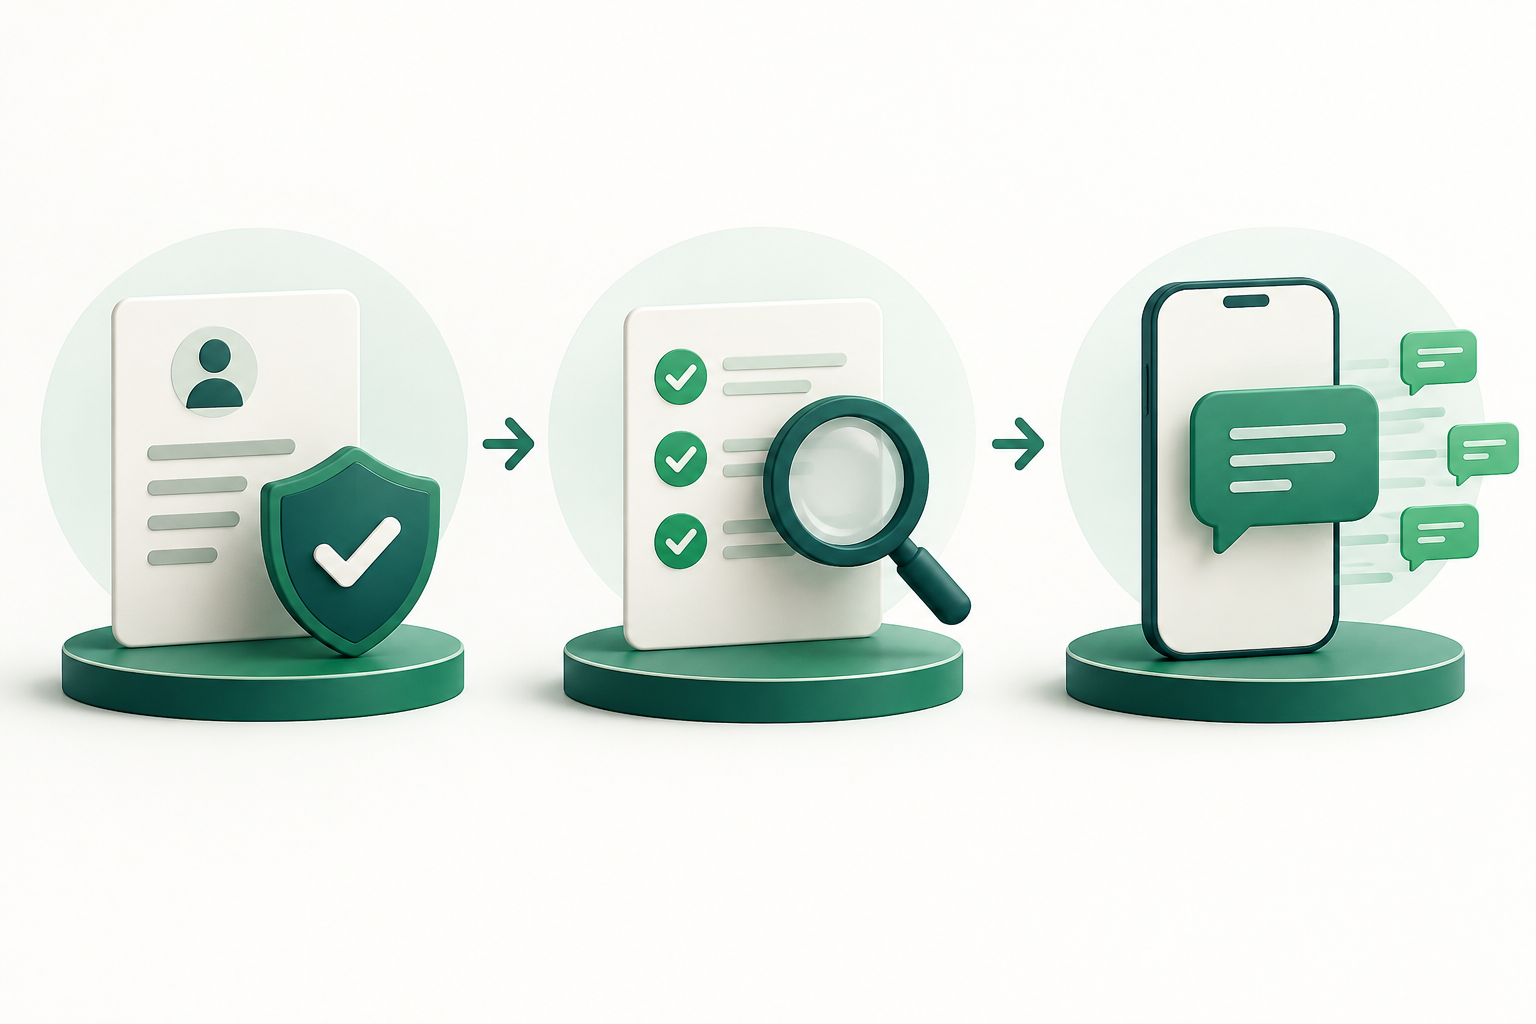
Keep useful, proportionate evidence of consent
Maintain a record that lets you reconstruct what was presented to the person and what action they took. Operational fields to consider include the date and time, phone number, capture method and context, language, wording or version of the request, affirmative action, campaign, and sender. Where appropriate and lawful, also retain an identifier or technical details of the capture.
The documentation should make it possible to verify the scope, not merely show a generic “accepted” flag. Save the version of the consent experience and link the event to the specific purpose. Restrict access and retention periods in line with your privacy obligations and applicable law.
In the European Union, where processing is based on consent, the GDPR requires organizations to be able to demonstrate it and provides that withdrawing consent must be as easy as giving it. The ePrivacy Directive and its national transpositions may also be relevant to SMS marketing; do not assume that one standard applies in every country.
- Record evidence as a dated event, not just an editable field with no history.
- Link the evidence to a purpose, campaign, and sender.
- Document changes to wording or scope so you can distinguish consents obtained under different conditions.
Centralize suppression and define its scope
A suppression list that can be checked helps prevent a contact who asked not to receive messages from being reintroduced through an import or another route. You do not need to retain more information than necessary: keep the minimum data needed to recognize the contact and block the affected purpose, with appropriate access controls.
The scope of an opt-out can vary. A person may withdraw permission for a particular channel or activity; a request or a rule may require a broader scope. Clearly record whether suppression applies to a program, brand, sender, purpose, channel, or all of them, and apply the broadest interpretation that fits the request and applicable rules.
If multiple providers, senders, or systems are involved, your own list should be the shared operational reference. A platform’s local lists can be useful, but they should not become the only record of the preference.
- Check suppression when importing contacts and before building a campaign.
- Check again just before queuing or sending, to catch opt-outs received after segmentation.
- Do not delete an opt-out record in a way that prevents future unwanted sends from being blocked.
Apply preferences before queuing each message
Define an eligibility check that brings together current consent, the message purpose, the sender or brand, the channel, the jurisdiction, and applicable suppression records. If any of this information is unknown or outdated, do not turn uncertainty into permission: stop or hold the send for review until it is resolved.
For legitimate service, transactional, or authentication communications, do not assume that marketing rules apply in exactly the same way, or that labeling content “transactional” is enough to justify it. Classify the purpose and content, then validate the basis and local restrictions before sending.
Keep the check close to the queuing point. A segmented list created hours earlier may be outdated if an opt-out arrives or a preference changes in the meantime.
- Identify the content’s actual purpose, not just the template name.
- Assess SMS preferences separately from preferences for other channels when the request is channel-specific.
- Block the send if you cannot confirm that consent and suppression data are synchronized.
Process an opt-out as a complete workflow
An opt-out may arrive by SMS reply, link, customer service, or another enabled method. The process should identify the contact, interpret the scope, record the event, and update the central source before allowing further sends covered by the request. Then propagate the status to platforms, lists, and senders involved in the same program.
You may send a brief confirmation when appropriate, but you should not require the person to take another action for the opt-out to be valid. The confirmation should not add promotional content. Retain the time received, incoming channel, scope applied, and propagation result as operational information, limited to what is necessary.
Specific deadlines depend on applicable rules. For example, in the United States, FCC rules recognize reasonable methods of revocation and provide a maximum period of ten business days for certain covered requests, while also allowing a one-time confirmation under specified conditions. The application of revocations across unrelated subjects has a limited temporary exemption; do not interpret it as suspending other obligations.
- Receive and record the opt-out.
- Determine and store its scope.
- Block new messages covered by the request and propagate the change to relevant systems.
- Confirm the opt-out without requiring an additional action, where appropriate.
Protect the process against bulk uploads and concurrent changes
Old imports should not reactivate suppressed contacts or silently replace a more recent status. Compare each imported record with the preference source and treat changes as identifiable events, with a verifiable result for each contact.
To reduce concurrency errors, use event identifiers, versioned states or timestamps, and idempotent operations. If an opt-out arrives while a campaign is being prepared, the final check before sending should take precedence. If you cannot confirm which status is current, block the send and resolve the discrepancy.
Reactivation should depend on a new affirmative consent signal with a defined scope, not on an opt-out being absent from another database. Explicitly propagate that new signal to the systems that need to reflect it and retain its evidence.
- Test imports with authorized contacts, suppressed contacts, and conflicting statuses.
- Log errors for each contact rather than treating an entire upload as successful.
- Prevent older synchronization processes from overwriting later opt-out events.
Measure operational controls, not supposed guarantees
Metrics help identify process failures, but they are not, by themselves, a certification of compliance. Build internal indicators that help investigate what happened and where propagation broke down.
Regularly review exceptions: an opt-out received but not applied, a send blocked because of outdated status, or a contact reappearing after an import requires root-cause analysis and correction. Keep enough traceability to audit the result without accumulating unnecessary personal data.
- Opt-outs received versus opt-outs applied.
- Attempts blocked because of suppression or insufficient evidence.
- Synchronization failures and records with conflicting statuses.
- Exceptions investigated, causes identified, and corrective actions taken.
Assign responsibilities and review local rules
The sender remains operationally responsible for checking authorization, purpose, and suppression, even when connectivity or transport is delegated to a platform. Providers may offer blocking and management tools, but those functions do not replace the sender’s evidence or compliance decisions.
Define who captures consent, who processes opt-outs, who maintains the central source, and who investigates errors. Include in operational agreements how events are communicated, which identifiers are used, and how incidents and provider changes are handled.
Before launching or expanding a program, review the requirements for each jurisdiction, message type, and relationship with the recipient. CAN-SPAM concerns commercial email and is not, by itself, sufficient to define A2P SMS controls.
- Advertiser or sender: evidence, purpose, and eligibility decision.
- Platform: apply configured controls, record outcomes, and propagate status as agreed.
- Connectivity provider: transport and available technical controls; it does not assume or create consent.
Frequently asked questions
Does a technically available route mean I can send the SMS?
No. Routing capability or a favorable technical response does not demonstrate current consent or that the send is eligible. Check authorization, purpose, preferences, suppression, and applicable rules before queuing.
Should I retain the phone number of someone who opted out?
You may need to retain the minimum data required to recognize the request and prevent future sends covered by it. Limit the information, access, and retention period in line with applicable obligations.
Does opting out of SMS also block email?
Not necessarily. The scope depends on the request and applicable rules. Record whether the opt-out applies to SMS, an activity, a brand, or a broader scope, and apply it accordingly.
Can an imported list reactivate a suppressed contact?
It should not. Check imports against the current suppression source. To reactivate a contact, require a new affirmative consent signal with a defined scope and explicitly propagate that event.
What should I do if I cannot confirm the latest status?
Block or pause the affected send until the discrepancy is resolved. Sending based on uncertain synchronization may disregard an opt-out or an updated preference.
Sources consulted
- FCC 24-24: Rules and Regulations Implementing the TCPAFederal Communications Commission
- FCC DA 26-12: extensión limitada de la exención sobre revocación entre asuntos no relacionadosFederal Communications Commission
- CTIA Messaging Principles and Best PracticesCTIA
- Reglamento General de Protección de Datos, Reglamento (UE) 2016/679Unión Europea, EUR-Lex
- Directiva 2002/58/CE sobre privacidad y comunicaciones electrónicasUnión Europea, EUR-Lex
- Respect people's preferencesInformation Commissioner's Office
- Twilio Messaging PolicyTwilio
- Consent Management APITwilio
- CAN-SPAM Act: A Compliance Guide for BusinessFederal Trade Commission