Shared Dependencies in A2P SMS Routes: How to Spot Apparent Diversity
Two routes contracted from different providers do not guarantee resilience. Learn to record what is known, what is only declared, and what remains unknown before designing a backup.
What Route Diversity Means
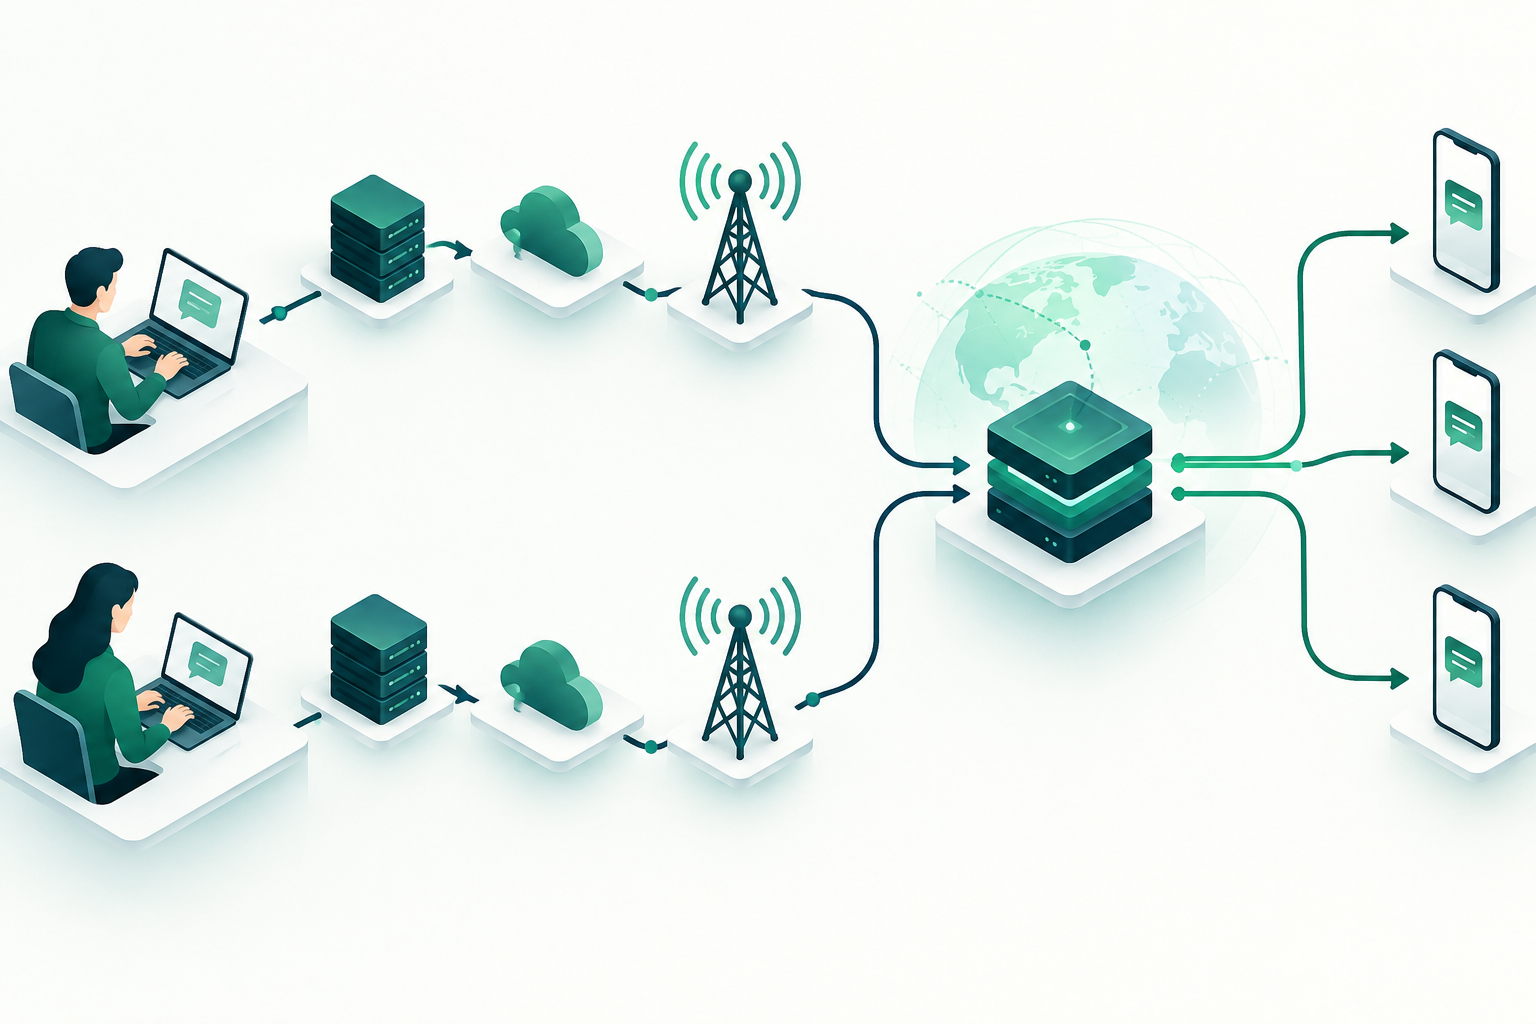
In an A2P SMS operation, having more than one configured route does not by itself demonstrate effective redundancy. Two commercial options may be distinct in a catalog yet still share some component of the chain. Without verifiable information about that chain, it is not possible to confirm or rule out that possibility.
It helps to distinguish three concepts: logical redundancy, when a system can select an alternative; declared diversity, when a provider states that routes are distinct; and verified diversity, when there is sufficient evidence to support a limited conclusion about relevant dependencies. None of these labels should be interpreted as a delivery guarantee.
- Do not treat the number of providers, connections, or route names as automatic proof of independence.
- Define which failure the setup is intended to tolerate—for example, the unavailability of a specific connection, platform, or destination.
- Specify the scope of any conclusion: the routes, destinations, period, and components for which evidence is available.
Layers That May Share Dependencies
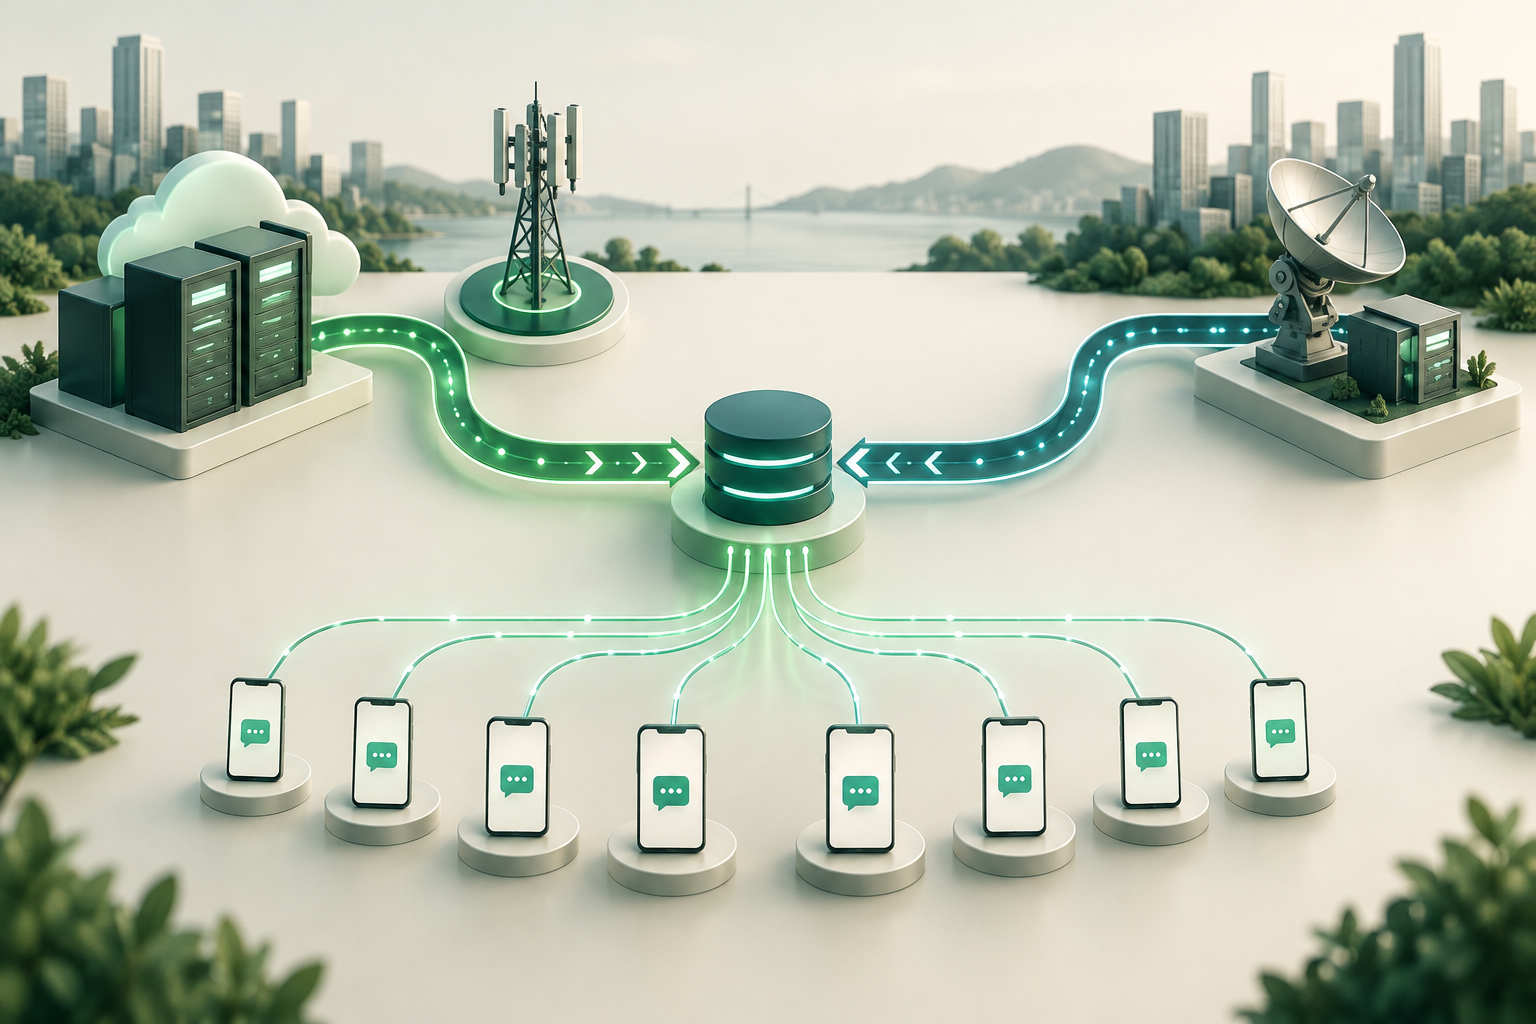
The map should cover the layers relevant to the operation without assuming that all routes use the same architecture. Possible questions include whether there is a common aggregator, a shared interconnection, a common management platform, or credentials that enable both routes. It may also be relevant to ask about the egress point or destination-side dependencies, provided the provider can describe them precisely.
This list is intended to help formulate questions, not to claim that any particular layer is shared. The evidence available for this guide does not establish the topology of A2P routes or provide a universal method for discovering it.
- Aggregation or intermediaries: Are there common entities in the chain, and what is the scope of the answer?
- Connection and platform: Do the routes use common interfaces, management systems, or operational infrastructure?
- Access: Do they share credentials, accounts, limits, or authentication mechanisms that could affect both?
- Destination: What is known about the interconnection to the operator or destination, and which parts of that information are declared or verifiable?
Build a Map With Provenance and Confidence Levels
Record each route separately and link every data point to its source. A commercial statement, a technical response, an observed configuration, and a test result do not have the same scope. Record when the information was obtained, who provided it, and which period or destinations it covers.
Use explicit categories rather than turning missing data into a claim: “provider-declared,” “observed in operation,” “confirmed within the stated scope,” or “unknown.” A provider may describe part of the chain; that response alone does not demonstrate how the rest works.
- Identify each route and its intended use without publishing sensitive data such as credentials.
- For each layer, record the claim, source, date, scope, and limitations.
- Distinguish observed facts from explanations provided after an incident.
- Mark any dependency for which there is insufficient information as unknown.
Review Incidents Without Confusing Correlation With Cause
If two routes show problems within a similar time window, the timing may justify an investigation, but it does not prove a shared dependency. Likewise, problems affecting certain destinations or similar delivery statuses do not, by themselves, identify the point of failure.
Retain the available operational records and compare observations by route and destination. Separate observed events from hypotheses, and document alternative explanations. A delivery status reported by a system is not necessarily equivalent to verified receipt on the recipient’s device.
- Record the incident window, routes involved, affected destinations, and reported statuses.
- Compare like-for-like data and note differences in coverage, volume, or configuration that may limit the comparison.
- Ask the provider for technical information about the scope of its diagnosis and the evidence supporting it.
- Do not attribute a common cause based only on timing correlation or similar results.
Test Alternatives With Controls and a Limited Scope
The available evidence does not establish a universal technical procedure for testing the independence of two A2P routes and does not support any specific method. The following suggestions are prudent ways to organize an assessment, not a validated procedure. Before conducting any test, define the hypothesis you want to evaluate and agree on the scope with providers and responsible teams. Use only legitimate traffic, with authorization and in accordance with applicable rules.
If the operation allows, it may be prudent to start in a controlled environment or with an agreed sample. Do not divert production traffic or send messages to recipients without authorization in an attempt to trigger a failure. As a recordkeeping practice, document the configuration, test window, destination or group of destinations, observed results, and limitations. A limited test can provide evidence only about that scenario at most; it does not demonstrate independence across the entire chain, all destinations, or all failure modes.
- As a precaution, define the objective, stop criteria, responsible parties, and scope before sending traffic.
- Ensure test messages and their recipients are authorized and legitimate.
- Separately record route selection, reported statuses, and any available independent confirmation.
- Do not extrapolate a one-off test to components, destinations, or periods it did not cover.
State the Level of Redundancy Without Overclaiming
A useful classification communicates both what is known and what remains unresolved. “Partial redundancy” may describe a setup with an alternative route but with relevant dependencies that are shared or unclear. “Unknown dependency” indicates that the information is insufficient to assess independence. “Verified diversity” should be used only with a precise scope and sufficient evidence to support the conclusion.
Do not present any label as a guarantee of availability or delivery. The evidence gathered may reduce uncertainty about specific components, but it does not automatically establish how the entire chain will behave.
- Logical redundancy: an alternative can be selected; its independence has not been established.
- Partial redundancy: a shared dependency is known, or relevant components remain unverified.
- Unknown dependency: the available information does not support a well-founded conclusion.
- Verified diversity: limit the claim to the routes, layers, destinations, and period covered by the evidence.
Action Plan and Questions for the Provider
Ask for answers that can be incorporated into the dependency map and that clearly state their scope. If an answer is partial, ambiguous, or cannot be shared, record that limitation; do not replace it with an assumption.
Review the map after operational changes or incidents that may affect the routes. The available evidence does not establish how dependencies are shared across A2P routes or validate a specific method for discovering them. Therefore, the questions and practices in this guide should be understood as prudent guidance, not as a validated or universal technical procedure.
- Exactly which components or intermediaries are covered by the description of each route?
- Are any shared dependencies between the routes known, and which destinations does the answer apply to?
- Which parts of the information are declarations, and what operational evidence can support them?
- What topology, configuration, or provider changes should be communicated, and how soon?
- What data will be available to investigate an incident, and what are its limitations?
Checklist for Maintaining the Map
A dependency map is useful only if it preserves the provenance of its data and is updated when conditions change. Do not assume an earlier answer remains valid indefinitely: reconfirm its scope when changes occur or when new signals justify a review. These are prudent documentation practices, not a validated technical method for proving independence.
As part of that review, you can:
- Update routes and owners after changes to configuration, provider, or connection.
- Review incidents and controlled tests; separate observations, declarations, and hypotheses.
- Confirm whether dependency responses are still current and record the review date.
- Keep unknowns explicit and avoid describing something as proven independence when it has not been verified.
Frequently asked questions
Do two different providers guarantee independent routes?
No. The providers’ identities do not prove that every component in the chain is distinct. Ask about relevant dependencies and record the scope and evidence for each response.
Does a simultaneous incident prove that the routes share infrastructure?
No. Timing is a signal to investigate, not proof of a common cause. Compare observations and request technical evidence without confusing correlation with causation.
Does a successful test prove complete diversity?
Not necessarily. A test provides evidence only about the scenario and scope it covered. It does not automatically establish independence across all components, destinations, periods, or failure modes.
What does it mean to mark a dependency as unknown?
It means the available information is insufficient to confirm or rule out whether two routes share that dependency. It is a prudent conclusion, not a claim that the dependency exists.
Does a DLR confirm that the recipient received the SMS on their phone?
Not by itself. A DLR is a status reported by a system; it should not be presented as independent confirmation of receipt on the device unless additional supporting evidence exists.
Sources consulted
- 3GPP specifications3GPP
- ITU-T E.164International Telecommunication Union
- GSMA resourcesGSMA